
Dir' MCP server
Commit Oct 15, 2026Allows an AI assistant to interact with a seawater desalination plant cyber range to teach OT security, analyze attack paths, and plan defenses.
Also known as SiteQ8/Dir
- Stars
- 0
- Tools
- 11
- Downloads, 30 days
- —
- Latest version
- —
- Last commit
- Oct 15, 2026
- License
- MIT
What is Dir' MCP?
Dir' allows an AI assistant to interact with a seawater desalination plant cyber range to teach OT security, analyze attack paths, and plan defenses. It exposes 11 tools, such as overview, list_units, list_zones.
Summary generated from the project's README
About Dir' MCP server
Teaching operational technology security through a simulated seawater desalination plant is what this server enables for cybersecurity defenders. It provides an AI assistant with read-only access to a complete cyber range model, including process units, defensive controls, and attack scenarios. By connecting an MCP client to the server via npx, an assistant can act as an instructor or planner using the same logic as the browser-based simulation.
Users can interact with specific tools like list_controls to see how defenses map to the National Cybersecurity Authority Operational Technology Cybersecurity Controls. The server allows an AI to run the plan_defense tool to simulate how chosen controls perform against specific kill chains, such as a TRITON style attack. It also provides access to a bilingual glossary and the Purdue model view to help users understand industrial automation security requirements. This setup is designed for educational purposes, helping students and professionals analyze attack paths and plan defenses within a controlled, fictional environment.
What you can do with it
- 1Simulate defensive outcomesAsk the assistant to run a specific attack scenario against a selected set of defensive controls to see the resulting plant state.
- 2Map defenses to regulatory standardsRequest a list of available defensive controls and their corresponding coverage of the NCA OTCC requirements.
- 3Analyze industrial attack pathsHave the AI explain the steps of a specific cyber attack scenario mapped to MITRE ATT&CK for ICS techniques.
- 4Evaluate security postureUse the assistant to calculate how much budget has been spent and how many attacks a specific set of controls can stop.
Written from the project's README. Every use case is checked against a quote from it.
Dir' MCP tools 11
Detected from the READMEoverviewlist_unitslist_zoneslist_controlslist_otcclist_scenariosget_scenarioplan_defenseassess_postureglossarysources
| overview | — | |
| list_units | — | |
| list_zones | — | |
| list_controls | — | |
| list_otcc | — | |
| list_scenarios | — | |
| get_scenario | — | |
| plan_defense | — | |
| assess_posture | — | |
| glossary | — | |
| sources | — |
Automated checks
Ran Nov 15, 2026Full report →Not verified yet. A server needs a score of 80, no serious finding, and enough data for us to check. How checks work · What to fix for more points

- Source repository linked and reachablesiteq8/dir is public and reachablegithub.com/siteq8/dir ↗Pass
- Package names this repository as its sourceNot checked
- Build provenance (Sigstore attestation)Not checked
- Open source license (OSI)MITspdx.org/licenses/MIT.html ↗Pass
- Commit or release in the last yearLast commit or release 2026-10-15github.com/siteq8/dir ↗Pass
- OpenSSF ScorecardNot checked
- Package name not close to a popular packageNot checked
- No critical advisory in the package or its dependenciesNot checked
- No hidden instructions to the model11 tool descriptions and the README read; no override phrases, credential paths or hidden charactersPass
- Destructive tools are labelledNo tool named like delete, drop or execPass
- Remote endpoint answers the MCP handshakeNot checked
README
View on GitHubدرع · Dir'
An open source seawater desalination plant cyber range for Saudi Arabia
ميدان سيبراني مفتوح المصدر لمحطة تحلية مياه بحر في السعودية
Open the live range → dir.3li.info
What this is
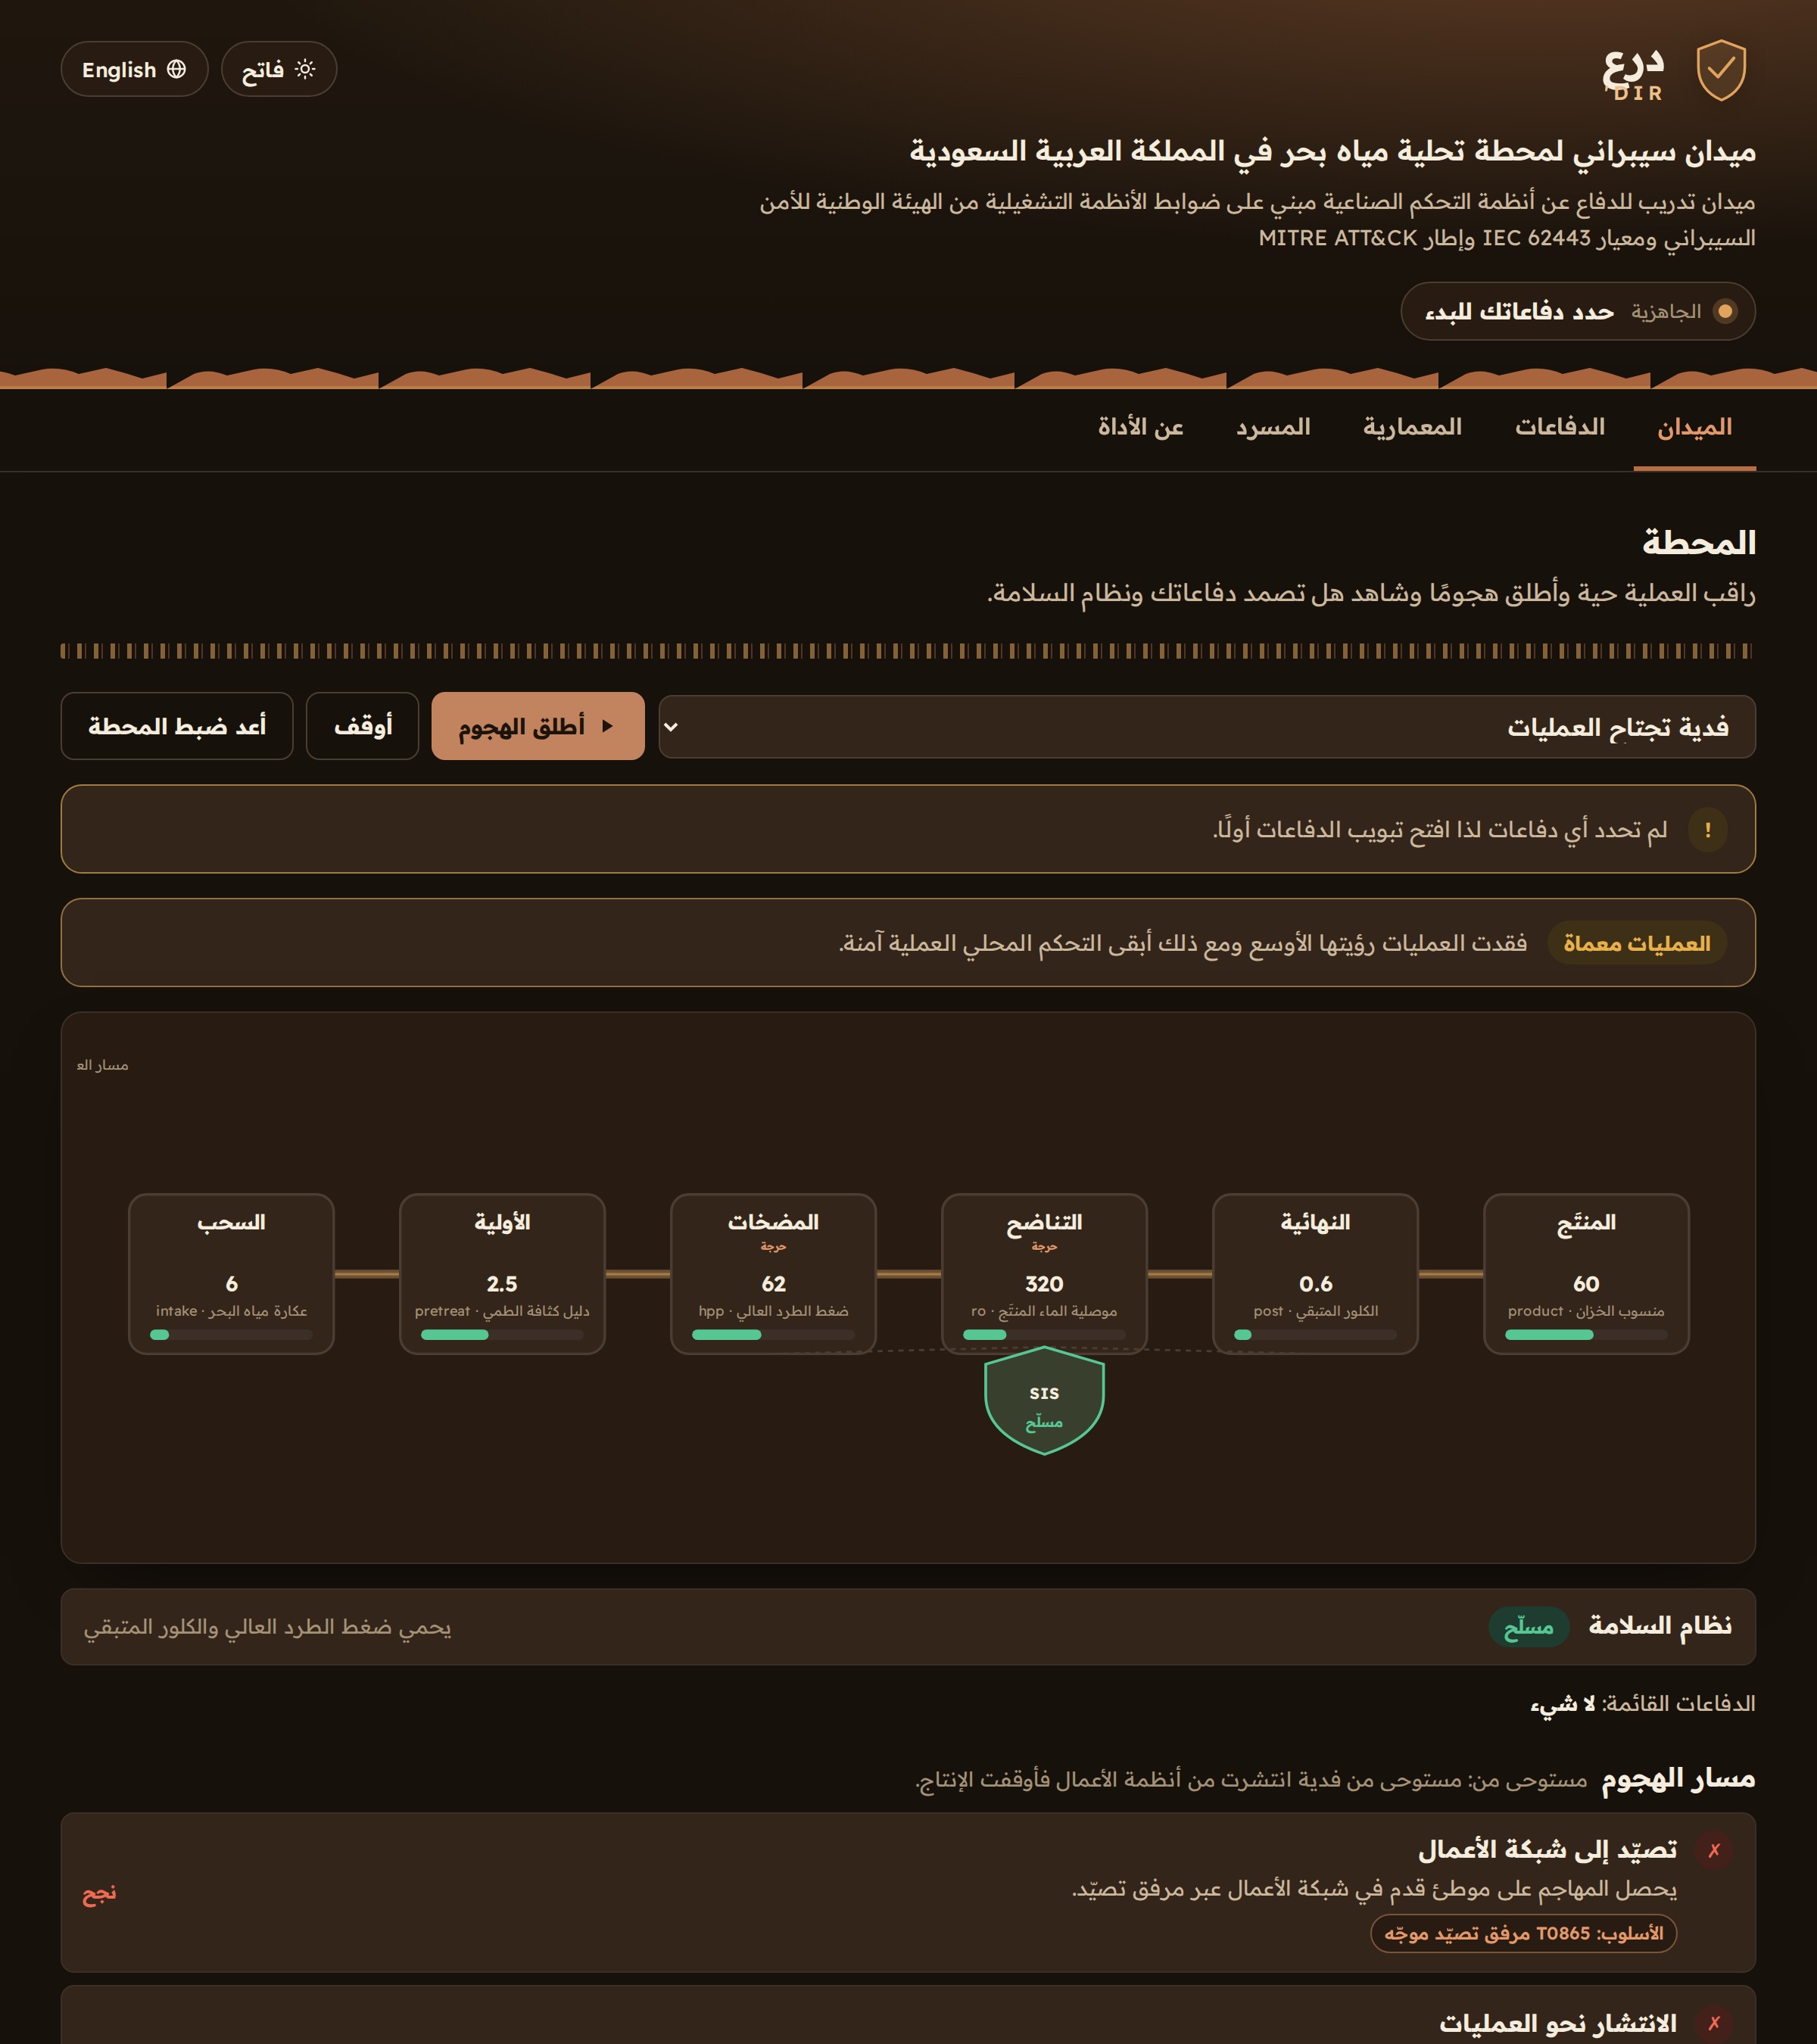
Dir' is a browser based cyber range for defenders of operational technology. It shows a fictional seawater desalination plant as a live process, lets you spend a limited budget on defensive controls, then launches realistic attacks and shows you the ending your defenses earned. The safety instrumented system is a first class character: in most scenarios it trips the plant to a safe state and diverts off-spec water to waste even when the attacker gets in, and only a specific safety focused attack can defeat it and let unsafe water reach the network.
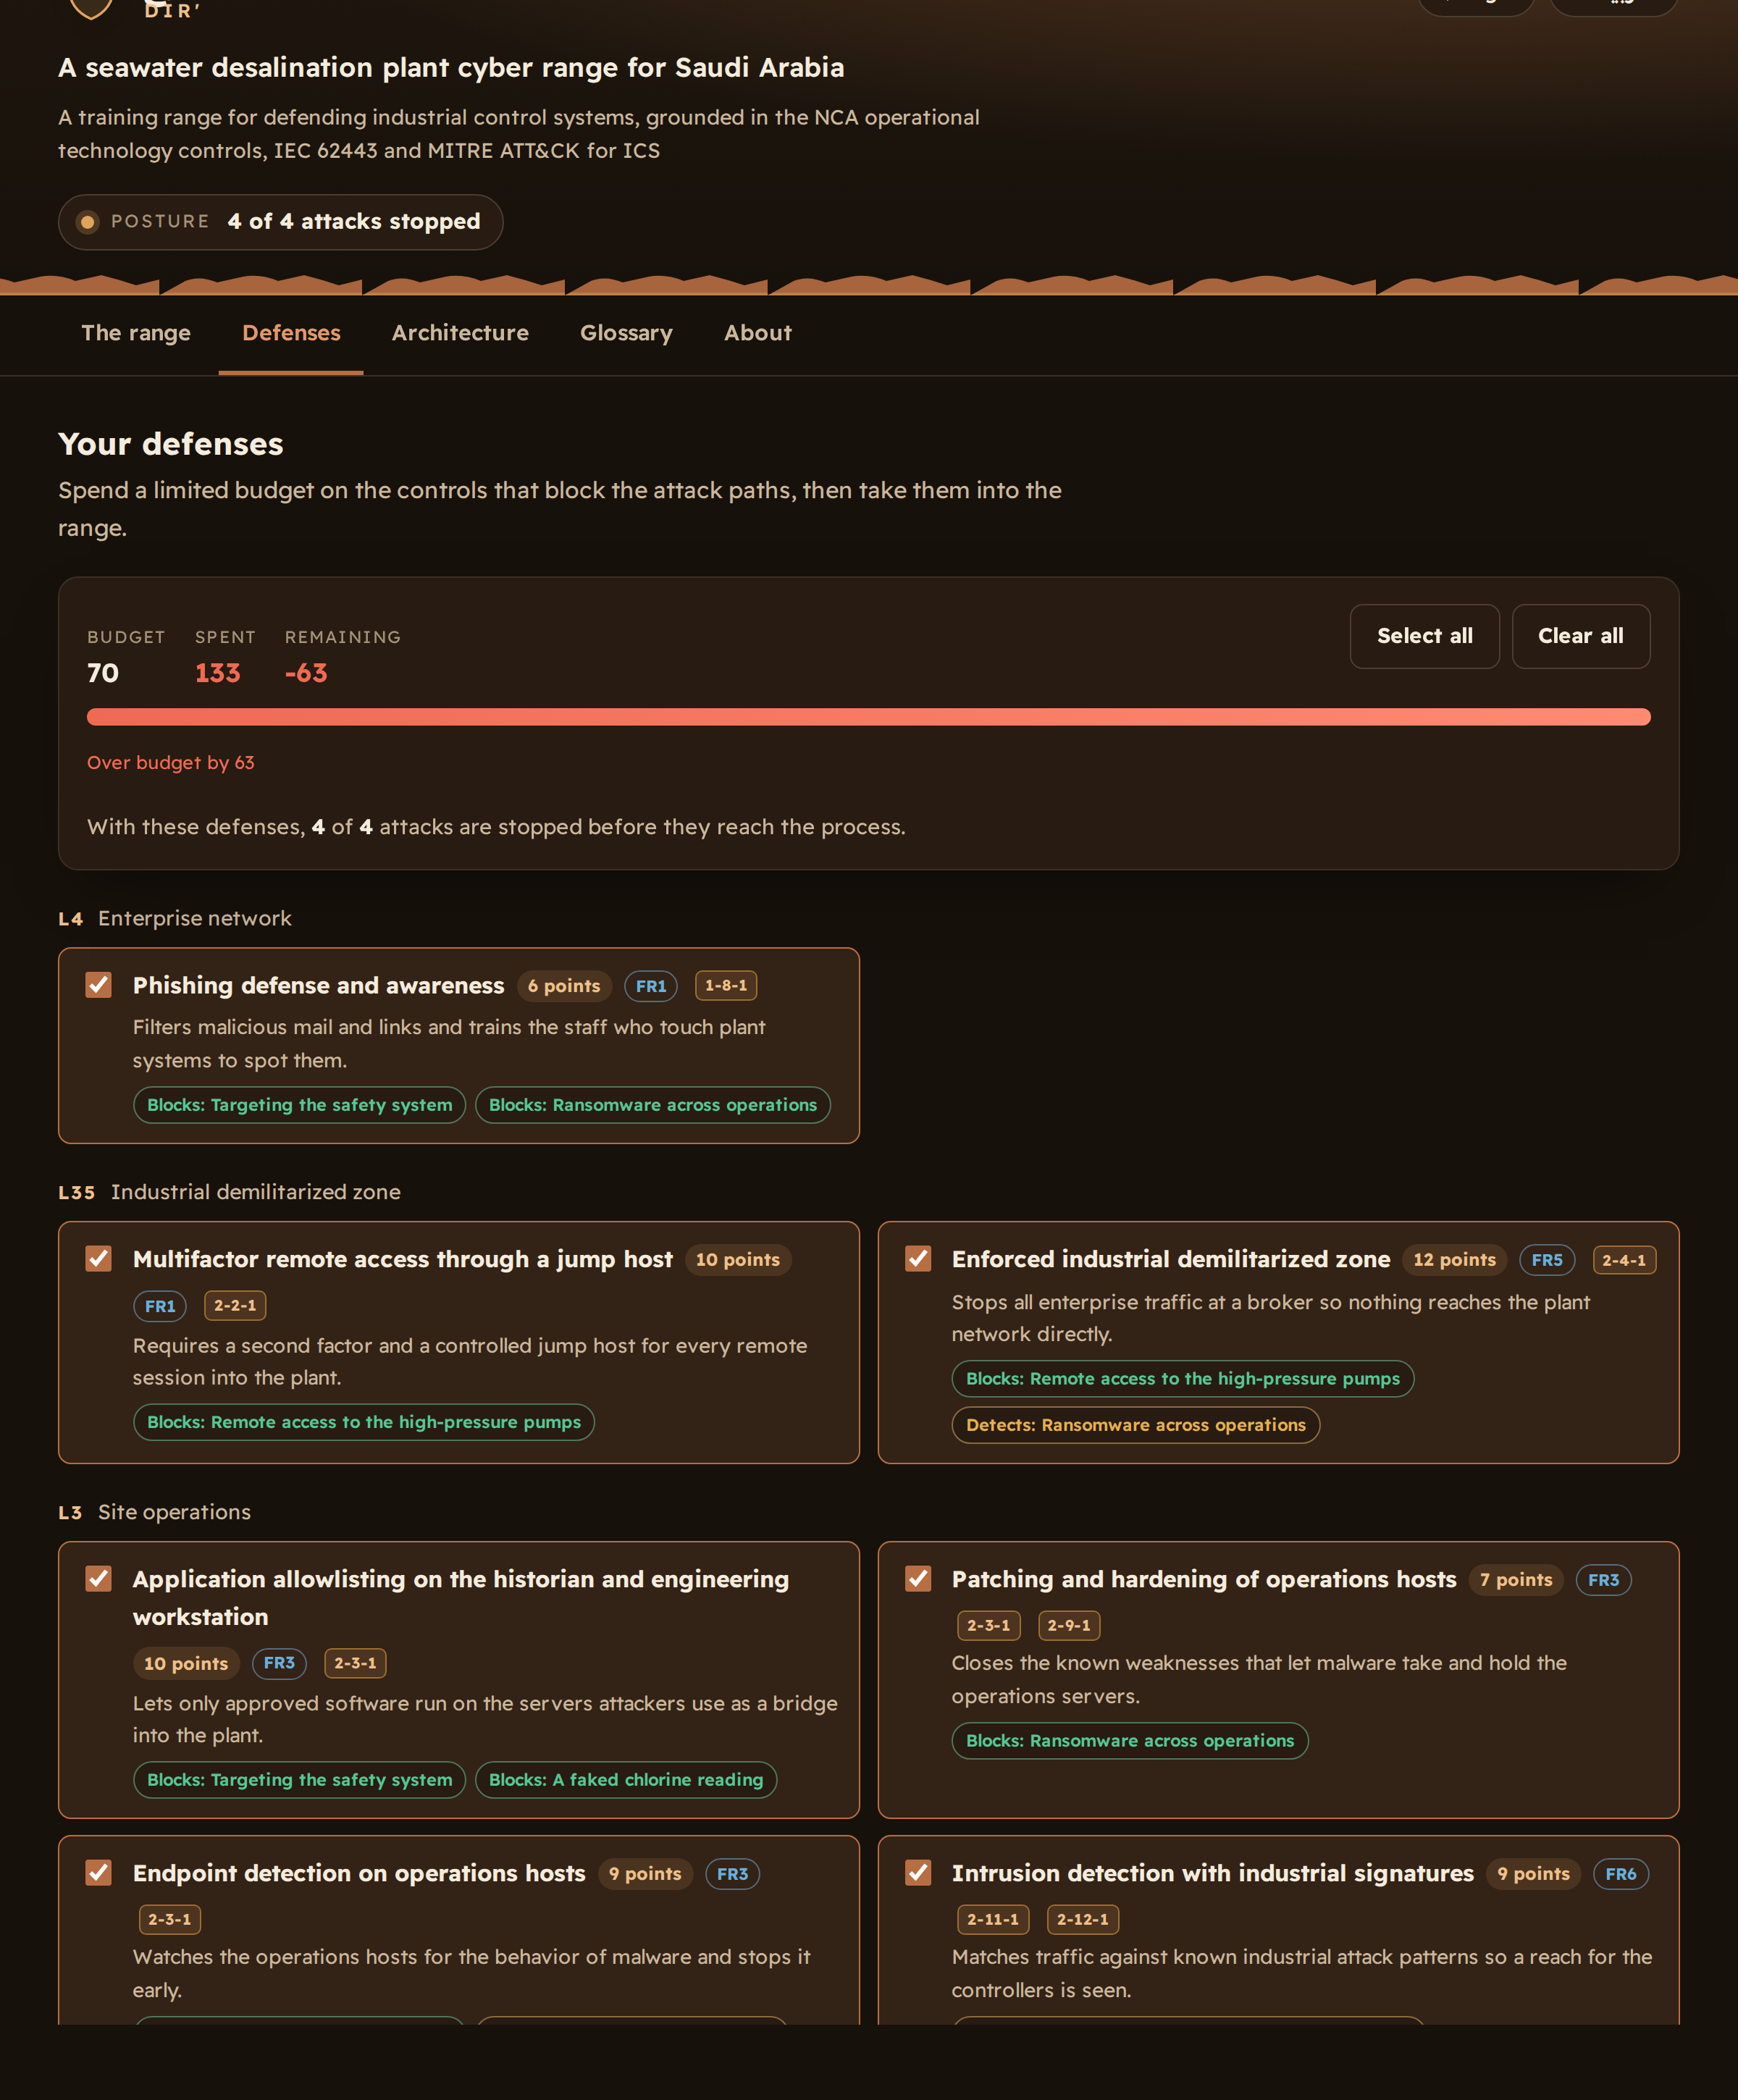
Every defensive control is mapped to the National Cybersecurity Authority Operational Technology Cybersecurity Controls, so the range doubles as a way to see OTCC coverage grow as you build. Everything is bilingual in Arabic and English, works offline as static files and ships with a Model Context Protocol server so an AI assistant can teach from the same model.
درع ميدان سيبراني في المتصفح للمدافعين عن أنظمة التشغيل الصناعية يعرض محطة افتراضية لتحلية مياه البحر كعملية حية ثم يتيح لك إنفاق ميزانية محدودة على ضوابط دفاعية ثم يطلق هجمات واقعية ويظهر لك النهاية التي حققتها دفاعاتك. نظام الأمان المجهز هو بطل القصة لأنه في معظم السيناريوهات يوقف المحطة إلى حالة آمنة ويحوّل الماء المخالف للمواصفة إلى الصرف حتى لو دخل المهاجم ولا يكسره إلا هجوم واحد يستهدف الأمان نفسه فيسمح للماء غير الآمن بالوصول إلى الشبكة.
The name
A dir' is the shield a defender raises in the field to cover themselves and those behind them. The plant is what you place the shield in front of. From behind the dir' you watch the attacker move along the kill chain, and you decide what to guard.
الدرع هو ما يرفعه المدافع في الميدان ليقي به نفسه ومن خلفه. المحطة هي ما تضع الدرع أمامه فمن خلف الدرع ترى المهاجم يتحرك عبر سلسلة الهجوم ثم تقرر ما الذي تحميه.
Features
- A live plant schematic with six process units from seawater intake to product water, real variable bands and a safety system that arms, trips or is defeated in front of you
- A defense budget that is smaller than the full catalog, so every choice is a tradeoff
- Four scenarios whose steps map to MITRE ATT&CK for ICS techniques, including a TRITON style attack on the safety system and a spoofed chlorine analyzer
- Outcomes that follow engineering logic: contained, a safe trip and diversion, an operational disruption, or unsafe water reaching the network
- Every defense mapped to the NCA OTCC, with a coverage view across the 47 controls and 23 subdomains
- An incident playbook for each scenario aligned to the NCA phases and reporting to the National Cybersecurity Authority
- A Purdue model view with the seven IEC 62443 foundational requirements
- A bilingual OT, ICS and desalination glossary
- A dark desert theme by default and a light theme, full keyboard access and a strict Content Security Policy
- A zero dependency MCP server that exposes the whole model as read only tools
Screenshots
The MCP server
Dir' ships an MCP server so any assistant that speaks the Model Context Protocol can read the plant, the controls, the attack paths, the playbooks and the OTCC mapping, and can run the same planner the site uses. It has no dependencies and it is read only.
Run it directly from the repository:
npx -y github:SiteQ8/Dir
Point your MCP client at that command:
{
  "mcpServers": {
    "dir": {
      "command": "npx",
      "args": ["-y", "github:SiteQ8/Dir"]
    }
  }
}
Tools
| Tool | What it returns |
|---|---|
overview |
What the range is, its counts and the training disclaimer |
list_units |
The six process units, their variable bands and the safety system |
list_zones |
The Purdue levels and the seven IEC 62443 foundational requirements |
list_controls |
The defensive controls with level, requirement, the OTCC controls they satisfy, cost and what they block or detect |
list_otcc |
The NCA OTCC reference: 4 domains, 23 subdomains and 47 main controls |
list_scenarios |
The scenarios with a short summary of each kill chain |
get_scenario |
One scenario in full with every step, its MITRE technique, the lesson and the playbook |
plan_defense |
Run a scenario against chosen controls and get each step state and the outcome |
assess_posture |
Budget spent, coverage by requirement, level and OTCC, and how many attacks a set of controls stops |
glossary |
The OT, ICS and desalination glossary, with an optional query in Arabic or English |
sources |
The authoritative sources behind the range |
Run locally
Requirements: Node 18 or newer.
git clone https://github.com/SiteQ8/Dir.git
cd Dir
npm run build       # assemble docs/data/bundle.json from data/src
npm test            # run the full test suite
npm run preflight   # build, test and check the site is release ready
Serve the site with any static server from the docs folder, for example:
python3 -m http.server 8000 --directory docs
How it is built
data/srcholds the plant, zones, controls, scenarios, incident phases, the OTCC reference, the glossary and every bilingual stringscripts/build.mjsassembles those intodocs/data/bundle.jsonand cross checks every referencedocs/assets/core.jsis the pure engine, shared by the site and the MCP serverdocs/assets/app.jsrenders the site and drives the live simulationmcp/server.mjsis the MCP servertestenforces the data model, the engine outcomes, the Arabic writing rules, the Content Security Policy and the MCP contract
Sources
- National Cybersecurity Authority, Operational Technology Cybersecurity Controls (OTCC-1:2022)
- National Cybersecurity Authority, Essential Cybersecurity Controls (ECC-2:2024)
- NIST SP 800-82 Guide to Operational Technology Security
- NIST SP 800-61 Computer Security Incident Handling Guide
- ISA and IEC 62443 series for industrial automation and control systems security
- MITRE ATT&CK for ICS
Disclaimer
The plant is fictional and composite. It is not any real facility and it carries no operational detail from any real plant. Dir' is for learning defensive engineering only. See NOTICE.md.
License
MIT. Copyright (c) 2026 Ali AlEnezi. See LICENSE.
Dir' MCP questions
What tools does Dir' MCP provide?
It exposes 11 tools, including overview, list_units, list_zones, list_controls, list_otcc.
What can the MCP server do?
The MCP server allows an AI assistant to read the plant model, controls, attack paths, playbooks, and OTCC mapping, and run the site's planner.
Is the MCP server interactive or read-only?
The MCP server is a zero-dependency, read-only tool.
How do I run the MCP server?
You can run it directly using npx with the command: npx -y github:SiteQ8/Dir