Lets an AI client observe a domain's public technology footprint, including email providers, identity indicators, SaaS services, and cloud infrastructure.
Also known as blisspixel/recon, recon-tool
- Stars
- 5
- Tools
- —
- Downloads, 30 days
- 4,398
- Latest version
- 2.27.0
- Last commit
- Nov 14, 2026
- License
- Apache-2.0
What is recon MCP?
recon lets an AI client observe a domain's public technology footprint, including email providers, identity indicators, SaaS services, and cloud infrastructure.
Summary generated from the project's README
About recon MCP server
Observing a domain's public technology footprint from inside an AI agent is what recon enables. Security researchers and developers can use this local MCP server to identify email providers, identity indicators, SaaS services, and cloud infrastructure without needing credentials, API keys, or performing active scanning. It works by analyzing public residue rather than conducting port scanning or application crawling.
Users can connect the server to clients like Claude Desktop, Claude Code, Cursor, VS Code, Windsurf, or Kiro. The tool provides evidence-backed observations through various output formats, including compact panels, structured JSON for automation, or plain text for screen readers. It also supports batch processing for multiple domains and delta commands to compare current findings against a cached baseline. Because it runs locally, it maintains privacy while providing high-signal insights into a target's digital presence.
What you can do with it
- 1Identify identity and email providersAsk the AI to find which identity vendor and email security controls a specific domain uses.
- 2Compare technology across domainsRequest a comparison of services used by different domains to find similarities or differences.
- 3Automate technology footprint collectionUse structured JSON output to feed domain reconnaissance data into automated workflows.
- 4Track changes in digital presenceCompare a domain's current technology stack against a previously saved baseline.
Written from the project's README. Every use case is checked against a quote from it.
How to install recon MCP
Formats verified 10 Nov 2026Add to CursorAdd to GooseInstall recon MCP in Claude Code
$ claude mcp add recon -- uvx recon-toolInstall recon MCP in Cursor
~/.cursor/mcp.json
{
  "mcpServers": {
    "recon": {
      "command": "uvx",
      "args": [
        "recon-tool"
      ]
    }
  }
}Install recon MCP in VS Code
.vscode/mcp.json
{
  "servers": {
    "recon": {
      "type": "stdio",
      "command": "uvx",
      "args": [
        "recon-tool"
      ]
    }
  }
}Install recon MCP in VS Code CLI
$ code --add-mcp '{"name":"recon","type":"stdio","command":"uvx","args":["recon-tool"]}'Install recon MCP in Claude Desktop
claude_desktop_config.json
{
  "mcpServers": {
    "recon": {
      "command": "uvx",
      "args": [
        "recon-tool"
      ]
    }
  }
}Install recon MCP in Codex
$ codex mcp add recon -- uvx recon-toolInstall recon MCP in Codex config.toml
~/.codex/config.toml
[mcp_servers.recon]
command = "uvx"
args = ["recon-tool"]
Install recon MCP in Gemini CLI
$ gemini mcp add -s user recon uvx -- recon-toolInstall recon MCP in Gemini settings.json
~/.gemini/settings.json
{
  "mcpServers": {
    "recon": {
      "command": "uvx",
      "args": [
        "recon-tool"
      ]
    }
  }
}Automated checks
Ran Nov 13, 2026Full report →Passed our automated checks. That is not a security audit: read the code and give the server the narrowest access it needs. How checks work

- Source repository linked and reachableblisspixel/recon is public and reachablegithub.com/blisspixel/recon ↗Pass
- Package names this repository as its sourcerecon-tool names blisspixel/recon as sourcepypi.org/project/recon-tool/ ↗Pass
- Build provenance (Sigstore attestation)Sigstore attestation for recon-toolpypi.org/project/recon-tool/ ↗Pass
- Open source license (OSI)Apache-2.0spdx.org/licenses/Apache-2.0.html ↗Pass
- Commit or release in the last yearLast commit or release 2026-11-03github.com/blisspixel/recon ↗Pass
- OpenSSF ScorecardOpenSSF Scorecard 8.5 / 10; weakest: Code-Review 0, Contributors 0, Branch-Protection 4scorecard.dev/viewer/?uri=github.com/blisspixel/recon ↗Pass
- Package name not close to a popular packageNo popular package one edit away from recon-toolPass
- No critical advisory in the package or its dependencies48 resolved dependencies checked; no critical advisoryosv.dev ↗Pass
- No hidden instructions to the model0 tool descriptions and the README read; no override phrases, credential paths or hidden charactersPass
- Destructive tools are labelledNot checked
- Remote endpoint answers the MCP handshakeNot checked
README
View on GitHubrecon


Point recon at a domain to see its public technology and identity footprint: email providers and controls, identity indicators, SaaS services, and cloud infrastructure. No credentials, API keys, or active scanning. Use the CLI for a quick lookup, versioned JSON for automation, or the local MCP server from an agent.
recon reports evidence-backed observations, not a complete inventory or a security verdict. A domain does not establish an organization's boundaries.
See the Output
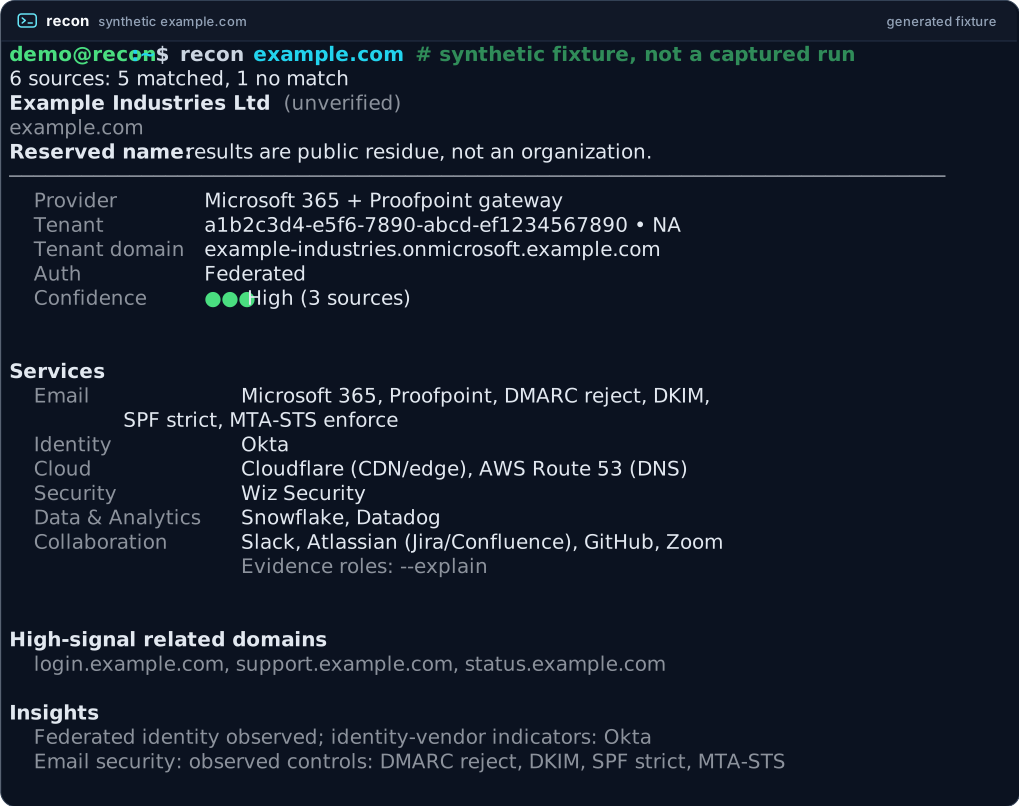
Synthetic illustration, generated, not captured. The real formatter renders
a deterministic, no-network fixture for Example Industries Ltd. No real
organization is depicted, and no live lookup of reserved example.com
reproduces this fixture.
demo@recon:~$ recon example.com    # synthetic fixture, not a captured run
6 sources: 5 matched, 1 no match
Example Industries Ltd (unverified)
example.com
Reserved name: results are public residue, not an organization.
──────────────────────────────────────────────────────────────────────────────
  Provider      Microsoft 365 + Proofpoint gateway
  Tenant        a1b2c3d4-e5f6-7890-abcd-ef1234567890 • NA
  Tenant domain example-industries.onmicrosoft.example.com
  Auth          Federated
  Confidence    ●●● High (3 sources)


Services
  Email            Microsoft 365, Proofpoint, DMARC reject, DKIM,
                   SPF strict, MTA-STS enforce
  Identity         Okta
  Cloud            Cloudflare (CDN/edge), AWS Route 53 (DNS)
  Security         Wiz Security
  Data & Analytics Snowflake, Datadog
  Collaboration    Slack, Atlassian (Jira/Confluence), GitHub, Zoom
                   Evidence roles: --explain


High-signal related domains
  login.example.com, support.example.com, status.example.com

Insights
  Federated identity observed; identity-vendor indicators: Okta
  Email security: observed controls: DMARC reject, DKIM, SPF strict, MTA-STS
Quick Start
macOS / Linux:
curl -fsSL https://raw.githubusercontent.com/pueo-labs/recon/main/scripts/install.sh | bash
Windows (PowerShell):
powershell -NoProfile -ExecutionPolicy Bypass -Command "irm https://raw.githubusercontent.com/pueo-labs/recon/main/scripts/install.ps1 | iex"
The installer sets up recon for your user account, including Python when needed.
Open a new terminal afterward. Python 3.15 is the default development and release
runtime; 3.11 through 3.15 remain supported. Already have a supported Python? Use
pip install recon-tool in a virtual environment, or uv tool install --python 3.15 recon-tool /
pipx install --python python3.15 recon-tool on managed distributions like Arch Linux and Omarchy.
For review-before-run instructions, other package managers, updates, and recovery,
see the installation guide.
recon --version      # offline install check
recon doctor         # online connectivity and installation diagnostics
Lookups make DNS queries visible to recursive and authoritative infrastructure.
MTA-STS is the only default target-owned HTTP request; Google CSE and BIMI
certificate probes require explicit --direct-probes. There is no port
scanning or application crawling. Replace the placeholder to start:
recon "<domain-you-want-to-review>"
Ordinary lookups may reuse the 24-hour result cache and say so when they do; a
result whose collection had unavailable sources is never reused. Use
--no-cache to bypass the cache for both reading and writing;
certificate-transparency enrichment has a separate cache. See
first lookup and cache behavior.
Common Commands
The bare command stays compact. Request evidence or structured output when needed:
recon example.com                      # compact panel
recon example.com --explain             # evidence and source status
recon example.com --json                # structured record
recon example.com --plain               # linear text for screen readers and grep
recon review example.com               # fresh, evidence-linked review bundle
recon batch domains.txt --json          # look up a supplied domain list
recon delta example.com                # compare with a cached baseline
recon update                           # update through the original package manager
These examples use reserved domains; real lookups will not reproduce the synthetic illustration above. For multi-domain reviews, recon describes observed similarities and differences without inferring ownership or a corporate relationship. See the evidence-first review workflow and batch guide.
Use with an Agent
The PyPI package installs the CLI and MCP runtime. Connect the local server to Claude Desktop, Claude Code, Cursor, VS Code, Windsurf, or Kiro:
recon mcp install --client=claude-desktop
recon mcp doctor
Restart the client and begin with manual tool approvals. Ask for one domain's email and identity indicators, or a service comparison across supplied domains. Missing evidence means "not observed", not "not used"; collection failures remain explicit. Local execution is the default, and the project does not operate a hosted service.
See MCP setup and supported clients and skills, plugins, and their validation status.
Omarchy Desktop Shell Integration
recon includes a thin, keyboard-first desktop shell plugin for Omarchy
located in integrations/omarchy/:
- Keyboard-driven workflow: focus domain input automatically, press
Enterto run bounded inspection, and pressCtrl+Dto toggle baseline delta comparison. - Direct process invocation: passes structured arguments directly (
["recon", domain, "--json"]) without shell interpolation. - Safe clipboard handling: pasting text never triggers an automatic network request.
- Zero background daemons: runs unprivileged inside Omarchy's Quickshell environment.
See integrations/omarchy/README.md for installation and shortcuts.
Documentation
| Need | Guide |
|---|---|
| Install, update, uninstall, or troubleshoot | Getting started |
| Find a command or flag | CLI reference |
| Build automation or hand off evidence | JSON schema, review bundles |
| Understand results and their limits | How it works, limitations, reporting observations |
| Linux and Omarchy environment setup | Linux / Omarchy guide |
| Check plans and shipped changes | Roadmap, changelog |
| Find architecture, security, research, or release procedures | Full documentation index |
Contributing and Support
Catalog corrections and documented vendor patterns are especially useful. Start with CONTRIBUTING.md for setup, verification, and contribution requirements; coding agents should also read AGENTS.md. For repeatable catalog work, start with the harness-neutral maintenance skill and offline example.
Use issues for bugs and feature requests. Keep public examples reserved and synthetic; never post evaluated company domains, tenant IDs, or per-domain results. See the private reporting paths and security policy. Intended for defensive use.
License
recon MCP questions
How do I add recon MCP to Claude Code?
Run claude mcp add recon -- uvx recon-tool in your terminal. Add --scope user to make it available in every project.
How do I add recon MCP to Cursor?
Open ~/.cursor/mcp.json and add the server under mcpServers, using the Cursor config shown in the install section above.
Can I use recon with Claude Desktop or Cursor?
Yes, the MCP runtime allows you to connect the local server to clients like Claude Desktop, Claude Code, Cursor, VS Code, Windsurf, or Kiro.
Is the data provided by recon a complete security audit?
No, it reports evidence-backed observations rather than a complete inventory or a security verdict.