
Provides a local firewall and password manager to control MCP server access and manage secrets for AI coding agents.
Also known as wkoverfield/switchboard, @switchboard-mcp/cli
- Stars
- 0
- Tools
- —
- Downloads, 30 days
- —
- Latest version
- 0.2.3
- Last commit
- Nov 14, 2026
- License
- MIT
What is Switchboard MCP?
Switchboard provides a local firewall and password manager to control MCP server access and manage secrets for AI coding agents.
Summary generated from the project's README
About Switchboard MCP server
Securing AI coding agents like Claude Code and Codex from unauthorized tool access and plaintext credential exposure is what Switchboard enables. It acts as a local authority layer that manages MCP server connections and sensitive secrets through your operating system's keychain. By routing agent requests through a single controlled endpoint, it ensures that tools are only accessible when a valid, time-limited pass is active.
Developers use the CLI to scan repositories for high-risk bypasses, such as GitHub tokens stored in plaintext config files. The import command consolidates scattered configurations into a single guarded route, replacing raw tokens with named keychain references. Once configured, you can use the grant command to issue scoped, expiring permissions that automatically revoke after a set duration. Everything runs entirely on your local machine with no telemetry or hosted service requirements, providing a private audit log of every tool call made by your agents.
What you can do with it
- 1Identify credential security risksScan a repository to find MCP servers and plaintext tokens that bypass your security controls.
- 2Migrate plaintext secrets to keychainConsolidate existing MCP configurations and move sensitive tokens into the OS keychain using named references.
- 3Issue temporary agent permissionsProvide an AI agent with a scoped pass that only allows specific tools for a limited number of hours.
- 4Monitor agent tool usageReview a local audit log to see every tool call routed through the firewall.
Written from the project's README. Every use case is checked against a quote from it.
How to install Switchboard MCP
Formats verified 10 Nov 2026Add to CursorAdd to GooseInstall Switchboard MCP in Claude Code
$ claude mcp add switchboard -- npx -y @switchboard-mcp/cliInstall Switchboard MCP in Cursor
~/.cursor/mcp.json
{
  "mcpServers": {
    "switchboard": {
      "command": "npx",
      "args": [
        "-y",
        "@switchboard-mcp/cli"
      ]
    }
  }
}Install Switchboard MCP in VS Code
.vscode/mcp.json
{
  "servers": {
    "switchboard": {
      "type": "stdio",
      "command": "npx",
      "args": [
        "-y",
        "@switchboard-mcp/cli"
      ]
    }
  }
}Install Switchboard MCP in VS Code CLI
$ code --add-mcp '{"name":"switchboard","type":"stdio","command":"npx","args":["-y","@switchboard-mcp/cli"]}'Install Switchboard MCP in Claude Desktop
claude_desktop_config.json
{
  "mcpServers": {
    "switchboard": {
      "command": "npx",
      "args": [
        "-y",
        "@switchboard-mcp/cli"
      ]
    }
  }
}Install Switchboard MCP in Codex
$ codex mcp add switchboard -- npx -y @switchboard-mcp/cliInstall Switchboard MCP in Codex config.toml
~/.codex/config.toml
[mcp_servers.switchboard]
command = "npx"
args = ["-y", "@switchboard-mcp/cli"]
Install Switchboard MCP in Gemini CLI
$ gemini mcp add -s user switchboard npx -- -y @switchboard-mcp/cliInstall Switchboard MCP in Gemini settings.json
~/.gemini/settings.json
{
  "mcpServers": {
    "switchboard": {
      "command": "npx",
      "args": [
        "-y",
        "@switchboard-mcp/cli"
      ]
    }
  }
}Automated checks
Ran Nov 14, 2026Full report →Passed our automated checks. That is not a security audit: read the code and give the server the narrowest access it needs. How checks work

- Source repository linked and reachablewkoverfield/switchboard is public and reachablegithub.com/wkoverfield/switchboard ↗Pass
- Package names this repository as its source@switchboard-mcp/cli names wkoverfield/switchboard as sourcenpmjs.com/package/@switchboard-mcp/cli ↗Pass
- Build provenance (Sigstore attestation)No build attestation published for this releaseNot checked
- Open source license (OSI)MITspdx.org/licenses/MIT.html ↗Pass
- Commit or release in the last yearLast commit or release 2026-10-31github.com/wkoverfield/switchboard ↗Pass
- OpenSSF ScorecardNot checked
- Package name not close to a popular packageNo popular package one edit away from @switchboard-mcp/cliPass
- No critical advisory in the package or its dependencies148 resolved dependencies checked; no critical advisoryosv.dev ↗Pass
- No hidden instructions to the model0 tool descriptions and the README read; no override phrases, credential paths or hidden charactersPass
- Destructive tools are labelledNot checked
- Remote endpoint answers the MCP handshakeNot checked
README
View on GitHubSwitchboard
A firewall and password manager for your AI coding agents.


Switchboard controls what Claude Code and Codex can reach in a repo. It finds the MCP servers and tokens your agents can already touch, gets secrets out of plaintext config and behind named keychain refs, and puts each agent on a scoped pass that expires on its own.
Everything runs locally. No account, no hosted service, no telemetry.
What it does
switchboard scanshows which MCP servers and tokens agents can reach in this repo, and which routes bypass Switchboard entirely.switchboard importconsolidates scattered Claude/Codex MCP config into one Switchboard route, with timestamped backups and exact rollback commands.- Secrets live in your OS keychain as named refs. Config files carry
secretRef: "github/ci/token", never the token itself. switchboard grantputs the agent on a pass: named tools reachable, everything else denied, gone in a few hours.switchboard statusanswers whether a pass is live right now.switchboard revokeends one early.- Every tool call routed through Switchboard lands in a local audit log.
switchboard logsreads it.
Install
npm install -g @switchboard-mcp/cli
Or without installing:
npx -y @switchboard-mcp/cli@latest scan
Requires Node 22 or newer. Daily use is on macOS, CI runs on Linux, and a Windows keychain backend exists but gets less exercise.
Quickstart
Start in a repo where your agents already work:
$ switchboard scan

This looks like acme-app.

Detected:
- Codex Switchboard route missing
- Claude Switchboard route missing
- Claude direct MCP server "github" detected

Authority bypasses:
  high claude:github (github; direct-mcp-server, secret-env-name)

Warnings:
- 1 direct MCP bypass finding(s), including 1 high-risk finding(s), were detected.
That high-risk finding is a GitHub token sitting in plaintext in .mcp.json.
Move it behind Switchboard:
switchboard import --dry-run          # see the plan first
switchboard import --write --cleanup-client
switchboard secrets set <ref>         # store the token; import prints the exact command
switchboard install claude --write    # route the agent through Switchboard
Import rewrites client config to a single Switchboard route, replaces the
plaintext token with a named keychain ref, and leaves a backup plus the exact
rollback command. Import never reads secret values itself; the secrets set
step is where the token actually enters your keychain. Then scope the agent:
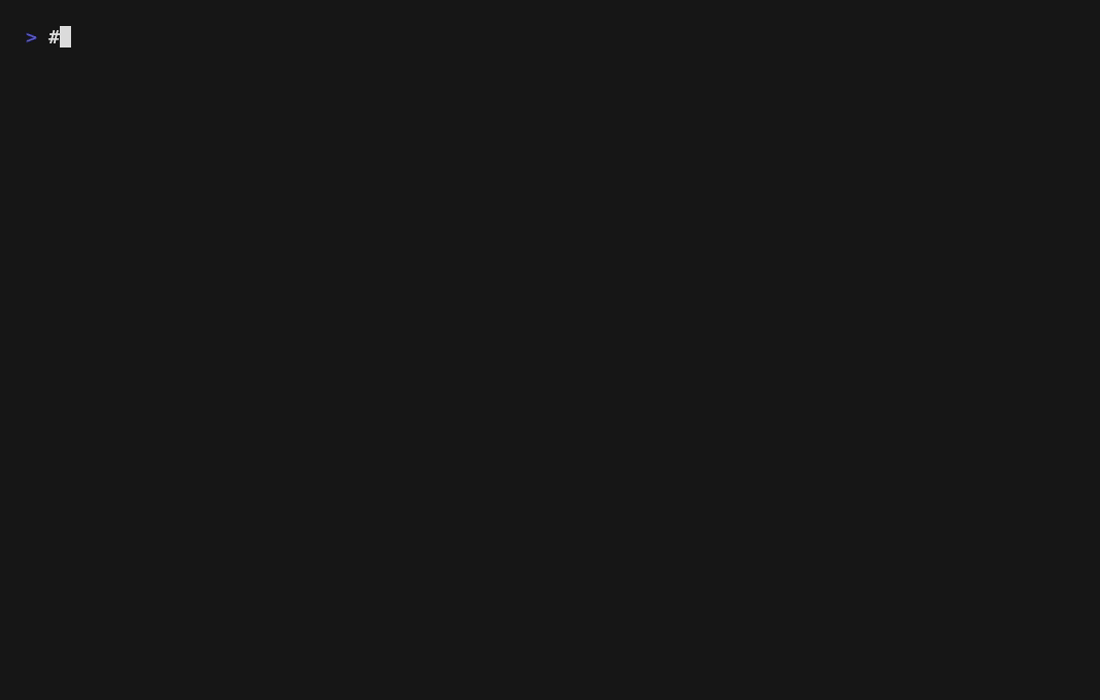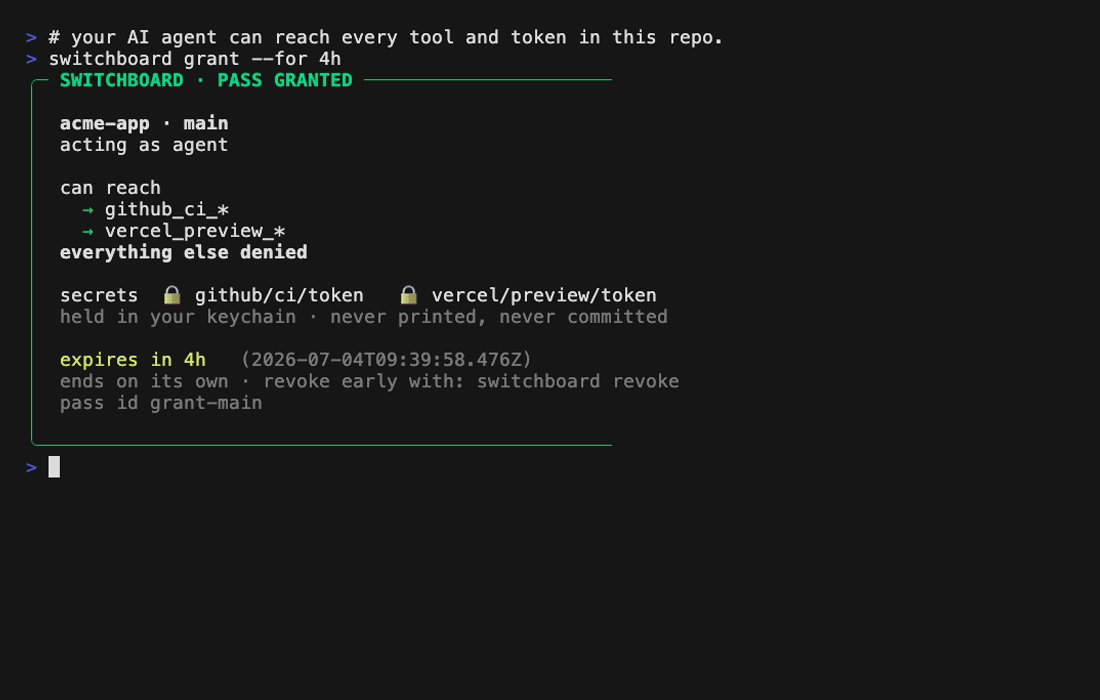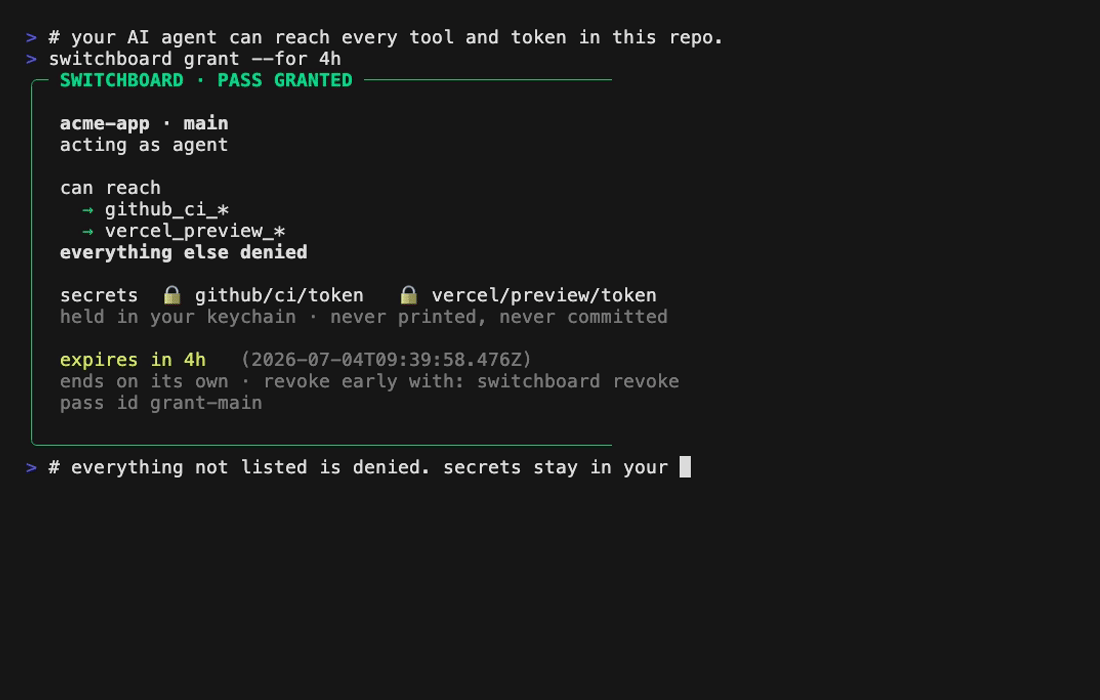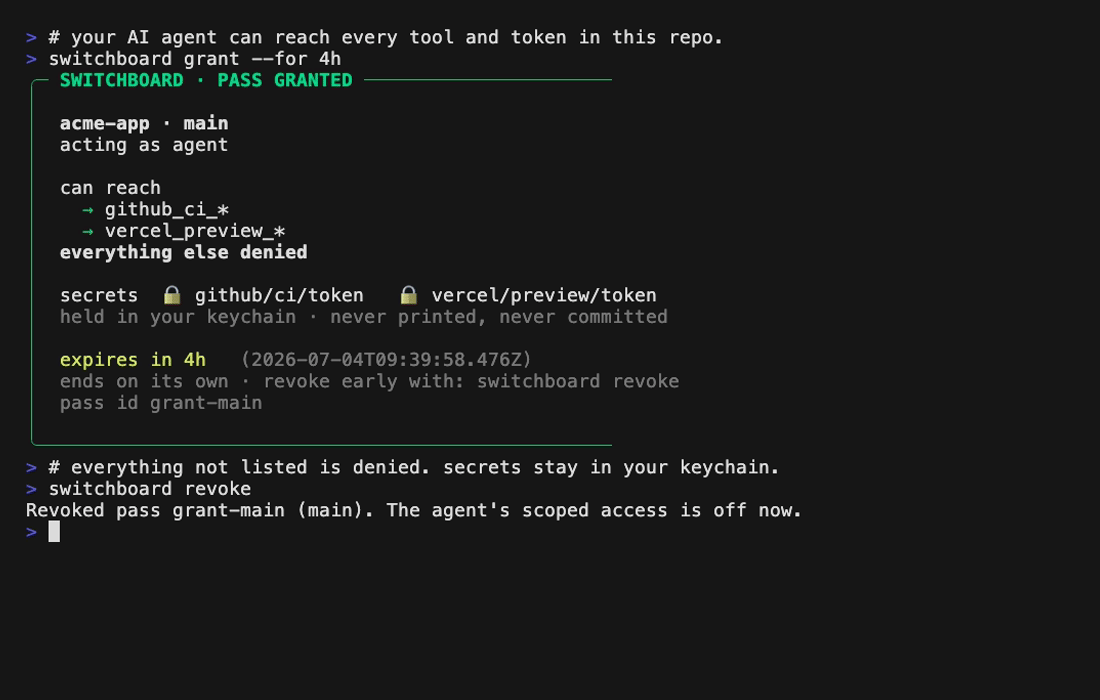
switchboard grant --for 4h
You get the pass above. When you want it gone early:
$ switchboard revoke
Revoked pass grant-main (main). The agent's scoped access is off now.
switchboard doctor tells you the next thing to fix at any point. If a repo
has no MCP config yet, switchboard setup github-ci starts from a safe
provider template instead.
What Switchboard does not do
- It is not a sandbox. Switchboard governs the paths routed through it:
Switchboard MCP endpoints and
switchboard run. An agent with raw shell access, a provider CLI, a browser session, or a direct MCP route can bypass it.switchboard scanreports those bypass routes so you can clean them up or accept them deliberately. - Backups keep your old config exactly as it was. If a token was in plaintext before import, the backup still contains it. Rotate old tokens after migrating, and keep backups private.
- A pass only binds routed agents.
switchboard grantsays so itself when no client is wired up yet, andswitchboard install <claude|codex>closes the gap. - It is alpha software. Local-first workflows, conservative claims, rough edges. The pass and audit contracts are versioned JSON, but expect change.
Commands
| Command | What it does |
|---|---|
switchboard scan |
Show what agents can reach in this repo, including bypass routes |
switchboard import |
Consolidate Claude/Codex MCP config into one guarded route |
switchboard grant / revoke |
Give the repo's agent an expiring scoped pass, or end it now |
switchboard status |
Is a pass live right now, and which config is active |
switchboard doctor |
Check the setup and print the next thing to fix |
switchboard setup <preset> |
Guided setup from a provider safety template (switchboard presets list shows them) |
switchboard auth <preset> |
Store the provider token for a preset in the keychain |
switchboard secrets |
Set, list, remove, and doctor named secret refs |
switchboard run |
Run an allowed provider command with pass-scoped credentials and audit |
switchboard install <client> |
Route Claude Code or Codex through Switchboard (add --scope user for one server across every repo) |
switchboard pass |
Create and inspect task-scoped passes with leases, gates, handoffs |
switchboard approvals |
Review and decide approval-gated tool calls |
switchboard tools |
List the tool surface a pass exposes |
switchboard logs |
Read the local audit log |
switchboard dashboard |
Local read-only dashboard: live passes, denials, audit stream |
switchboard audit |
Repo authority posture report, exportable as JSONL |
Commands that report state take --json for scripts and harnesses, with
versioned schemas. switchboard <command> --help has the rest.
How it works
Switchboard reads layered YAML config (global, then .switchboard.yaml, then
.switchboard.local.yaml). Each profile names an upstream MCP server and the
secret refs it needs. At runtime, Switchboard mounts permitted profiles as one
MCP endpoint, resolves secret refs from the OS keychain only at launch, and
namespaces every tool so a pass can allow github_ci_* and deny everything
else. Passes, approvals, and audit entries are plain local files that reference
secrets by name, never by value.
Secret storage uses OS keychain backends by default. Plaintext fallbacks exist
for dev machines and CI, and require an explicit
SWITCHBOARD_ALLOW_UNSAFE_SECRET_BACKENDS=1 opt-in.
For harnesses and subagent systems
switchboard pass create --from github-ci --json returns a
workspaceLease.mcpLaunch payload: the exact command to launch a
pass-scoped stdio MCP endpoint, plus the pass policy and lease. Switchboard
grants and audits authority; your harness owns scheduling, retries, and agent
processes. JSON contracts are documented in
docs/use-cases/harness-json-contracts.md.
Alternatives
- Project MCP config alone works, but it is static wiring with tokens in files. Switchboard imports that wiring, moves the tokens, and adds scoped expiring access on top.
- Docker MCP Gateway and MCP runtimes run and package MCP servers well. Switchboard is the local authority layer above them, deciding which profile, tools, and lease an agent gets for a task. A gateway can be an upstream behind a Switchboard profile.
- Hosted tool platforms (Composio, Arcade) offer managed OAuth and broad SaaS coverage. Switchboard is local-first for coding-agent repos: local secrets, local audit, no hosted dependency.
- Just giving the agent a token is fast until the token is broad, live, or copied into the wrong file. That is the failure mode Switchboard exists for.
Development
git clone https://github.com/wkoverfield/switchboard.git
cd switchboard
pnpm install
pnpm build
pnpm switchboard --help
pnpm test
Contributions are welcome; see CONTRIBUTING.md, and report vulnerabilities privately per SECURITY.md.
Smoke tests and fresh-agent evals live in scripts/; CI runs the full set.
The top demo is a VHS tape: brew install vhs && pnpm build && vhs examples/switchboard.tape.
Deeper docs: quickstart,
threat model,
provider safety templates,
roadmap.
Agents can read these docs over MCP:
npx -y @switchboard-mcp/docs-mcp serves list_docs, read_doc, and
search_docs, and llms.txt is kept current. The landing and docs
site lives in site/ (static build, pnpm --filter @switchboard-mcp/site build).
License
MIT. See LICENSE.
Switchboard MCP questions
How do I add Switchboard MCP to Claude Code?
Run claude mcp add switchboard -- npx -y @switchboard-mcp/cli in your terminal. Add --scope user to make it available in every project.
How do I add Switchboard MCP to Cursor?
Open ~/.cursor/mcp.json and add the server under mcpServers, using the Cursor config shown in the install section above.
Is Switchboard a hosted service?
No, everything runs locally with no account, no hosted service, and no telemetry.
How are secrets stored in Switchboard?
Secrets are stored in your OS keychain as named references, ensuring that config files contain references rather than plaintext tokens.
Can Switchboard prevent an agent from bypassing it?
Switchboard is not a sandbox; it governs routed paths. It can detect and report bypass routes like raw shell access or direct MCP routes via the scan command.
What happens when I grant an agent access?
The agent is put on a scoped, expiring pass where only named tools are reachable and everything else is denied.