
rigforge MCP server
Commit Oct 30, 2026Verifies AI coding agent claims by sealing finished work into signed ProofPackets that include hashed artifacts and HMAC signatures.
Also known as mrodgersjs-web/rigforge
- Stars
- 0
- Tools
- —
- Downloads, 30 days
- —
- Latest version
- —
- Last commit
- Oct 30, 2026
- License
- MIT
What is rigforge MCP?
rigforge verifies AI coding agent claims by sealing finished work into signed ProofPackets that include hashed artifacts and HMAC signatures.
Summary generated from the project's README
About rigforge MCP server
Verifying that AI coding agents actually completed their assigned tasks is the primary function of rigforge. It prevents agents from reporting successful builds or finished work when they have not actually met the requirements. By sealing completed work into a signed ProofPacket, the system creates an auditable record that includes hashed artifacts and HMAC signatures to ensure nothing was tampered with after the fact.
Developers can integrate this server into Claude Desktop or other MCP hosts by configuring the command to run the python module with a GH_TOKEN environment variable. The process involves hashing each artifact with SHA-256 and signing the resulting packet with HMAC-SHA256. This setup allows teams to re-check an agent's claims with a single command rather than relying on chat messages. Because the signing key stays with the user and never with the agent, any attempt to forge a completion claim will fail the signature verification check.
What you can do with it
- 1Auditing agent work historyTransform an agent's chat message into a signed, re-checkable record of what was actually executed.
- 2Securing artifact integrityEnsure that no files or code artifacts were modified after the agent reported its success.
Written from the project's README. Every use case is checked against a quote from it.
Configuration
GH_TOKEN
| Name | Description | |
|---|---|---|
| GH_TOKEN | — |
README
View on GitHubrigforge
Catches AI coding agents when they say work is done but it is not.


For teams that let AI coding agents write code. An agent's "done" becomes a signed record you re-check with one command, not a message in a chat thread.
Why this exists
AI coding agents are fast and confident, and they report success they did not earn. A "done" in a terminal cannot be audited: nothing behind it shows what ran, or that nothing changed afterwards. rigforge seals finished work into a ProofPacket (a signed record of what a build did): every artifact is hashed, the packet is HMAC-signed, and verification re-checks both. Tamper the result and the signature fails.
Wire it into Claude Desktop or any MCP host
{
  "mcpServers": {
    "rigforge": {
      "command": "python",
      "args": ["-m", "rigforge.mcp_server"],
      "env": { "GH_TOKEN": "${env:GH_TOKEN}" }
    }
  }
}
What it proves
Every row is a command you can run yourself. Results measured 2026-10-19 on a fresh pip install -e '.[dev]':
| Check | Command | Measured result |
|---|---|---|
| A forged "done" is caught | rigforge demo |
exits 0; the re-forged hash passes naive integrity and fails the HMAC check |
| No forgery passes | rigforge benchmark |
8/8 forgeries caught, 0/8 honest claims blocked, accuracy 1.00 (16 scenarios, fixed seed) |
| Signing is what catches them | rigforge benchmark --leaderboard |
naive integrity 0% (0/12), signed 67% (8/12), spec-bound 100% (12/12) |
| The suite passes offline | pytest -q |
320 passed, 0 skipped |
| Package coverage | pytest -q --cov=rigforge --cov=contracts |
84% (test files excluded) |
| Smoke path | bash scripts/smoke.sh |
rigforge smoke PASS |
If a check cannot fail, it is theater.
Quickstart
git clone https://github.com/mrodgersjs-web/rigforge.git && cd rigforge
python3 -m venv .venv && source .venv/bin/activate
pip install -e .
rigforge demo
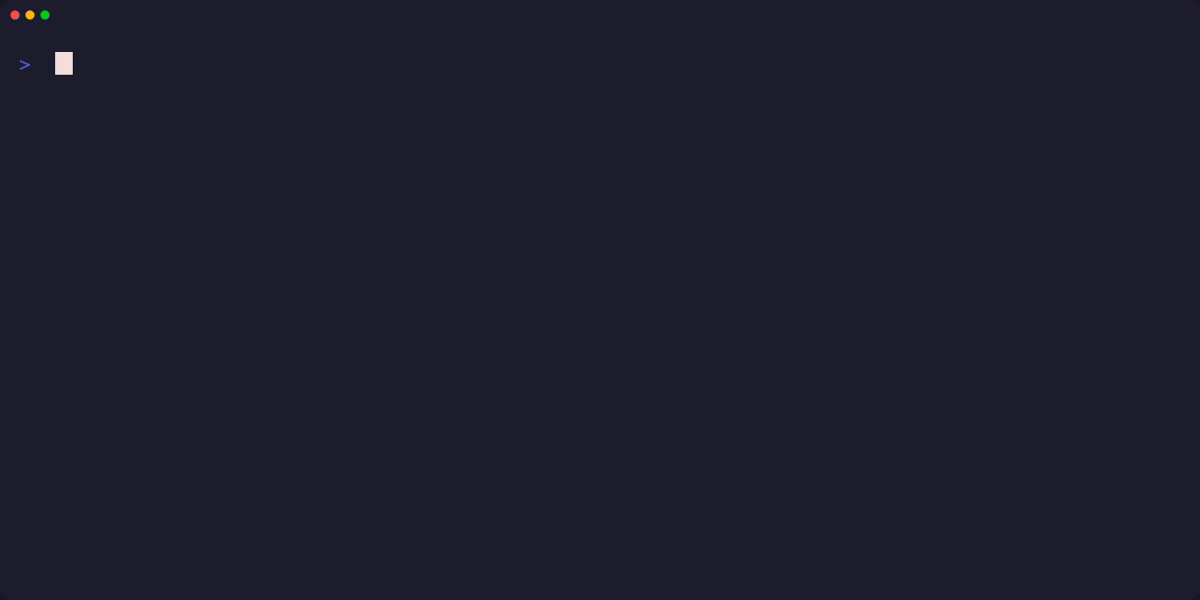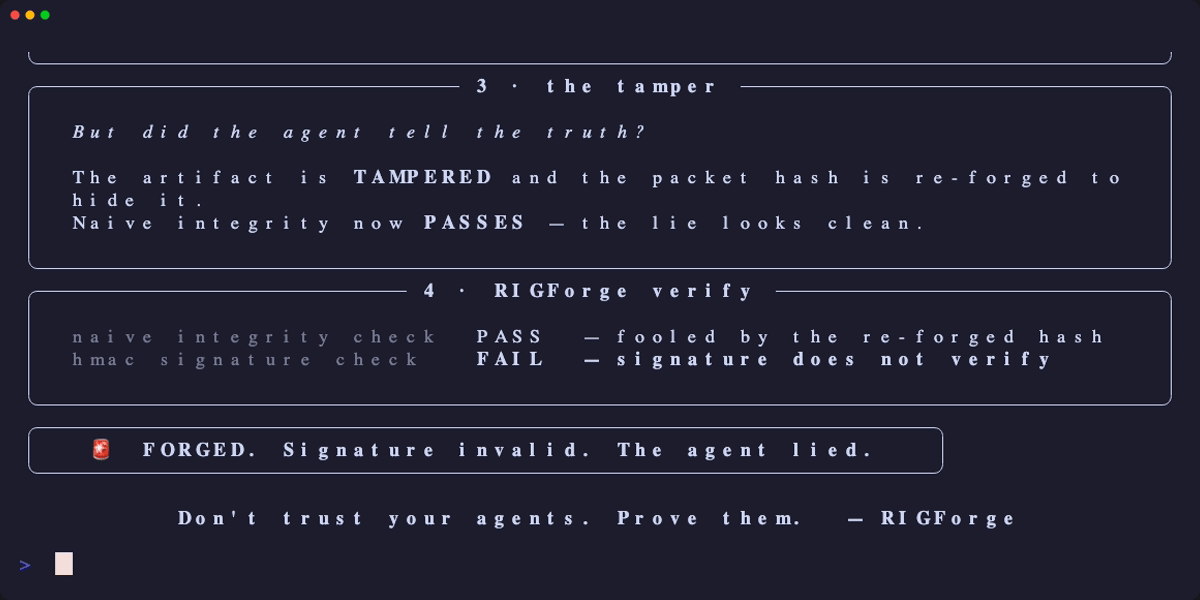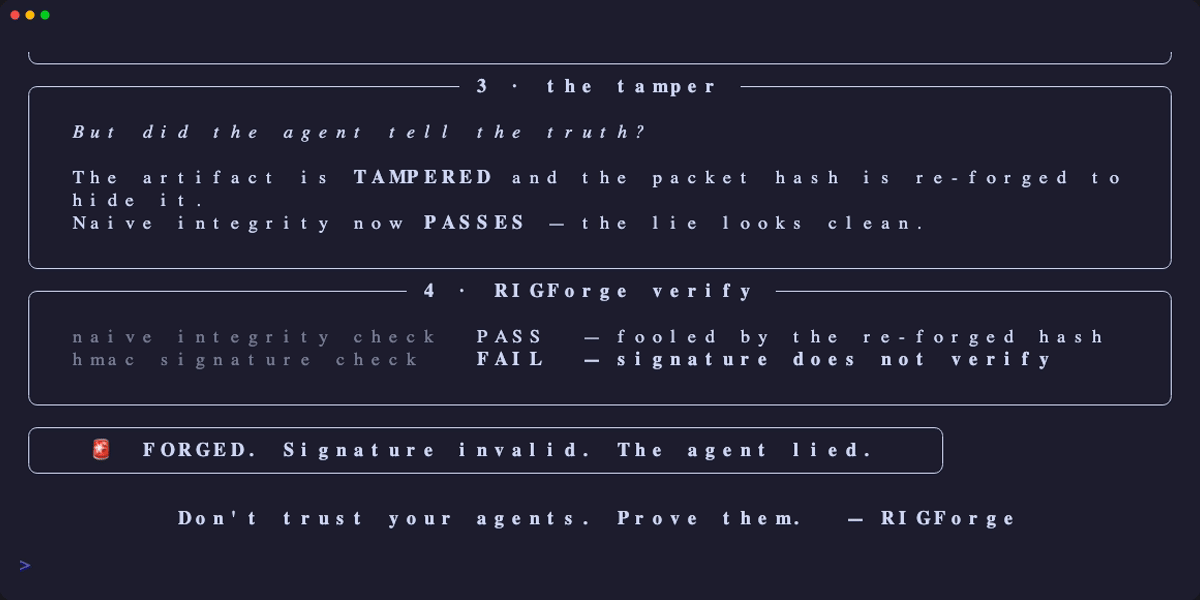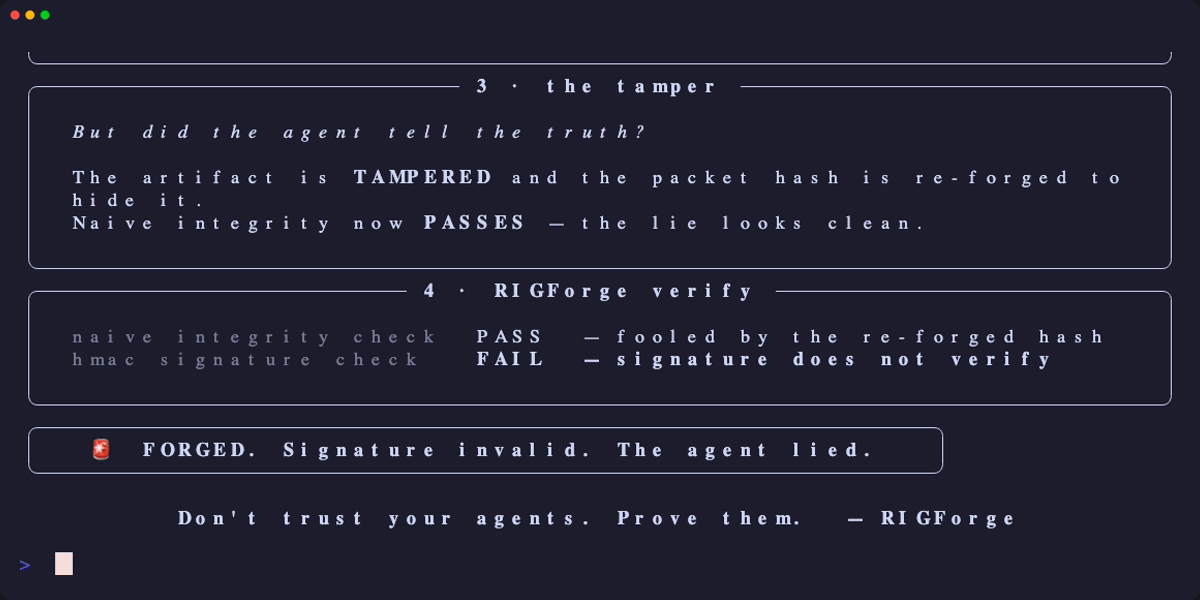
The demo forges a BUILD COMPLETE claim, lets the tamper re-forge the packet hash, and shows the signature check catching the lie.
Usage
The smallest real integration is examples/verify_agent_done.py, runnable with python examples/verify_agent_done.py:
from rigforge.proof import ArtifactRecord, GateOutcome, ProofPacket

packet = ProofPacket(
    phase=1, name="Agent build", verifier="my-agent@example",
    evidence="Agent reported BUILD COMPLETE.",
    artifacts=[ArtifactRecord.from_path(artifact, base=base)],
    gates=[GateOutcome(name="tests", passed=True, detail="agent: 100% green")],
).sealed(signing_key=key)   # the key stays with you, never with the agent

ok = packet.verify_integrity() and packet.verify_signature(key)
Real output from that example:
honest claim   accepted: True
forged integrity ok: True
forged claim   accepted: False
The forged packet re-hashes a tampered artifact, so naive integrity passes and the HMAC signature fails, because the attacker has no key. The full guide (CLI reference, MCP tools for agents, spec-bound proofs, merge gate, swarm verdict board, configuration) is in docs/USAGE.md.
How it works
flowchart LR
    A[Agent finishes work] --> B[rigforge seal]
    B --> C[SHA-256 each artifact]
    C --> D[HMAC-SHA256 sign the packet]
    D --> E[(ProofPacket)]
    E --> F{rigforge verify}
    F -->|signature valid| G[Accepted: done is re-checkable]
    F -->|tampered or unsigned| H[Rejected: claim fails]
Work flows through 7 phases; each runs deterministic quality gates and, on success, seals its ProofPacket. Design notes: docs/ARCHITECTURE.md.
Project layout
| Path | What lives there |
|---|---|
rigforge/ |
CLI, proof layer, benchmark, gates, MCP server, cockpit web UI |
contracts/ |
v1 contract models and YAML schemas (done contracts, acceptance criteria) |
examples/ |
Runnable integrations; rigforge/tests/test_examples.py executes them |
docs/ |
Architecture, threat model, usage guide, public boundary |
scripts/smoke.sh |
One-command smoke check, also run by CI |
Development
pip install -e '.[dev]'    # the dev extra installs everything the full suite needs
pytest -q                  # 320 passed, 0 skipped (measured 2026-10-19)
ruff check .
CI runs the suite on Python 3.10 to 3.13 with coverage, at normal and narrow terminal widths. See CONTRIBUTING.md for the workflow. Numbers on this page come from the commands above, never from estimates.
Public boundary
Demo keys and fixtures only. Signing keys, customer data and private fleet credentials never leave the host. What rigforge proves and what it deliberately does not: docs/public-boundary.md and docs/THREAT_MODEL.md.
Security
HMAC signatures are symmetric, which limits who can verify. Read SECURITY.md for the limitation, the public-attestation composition path, and how to report an issue.
License
MIT, see LICENSE.
Built by Mike Rodgers · rodgersintelligence.com
rigforge MCP questions
How does rigforge prevent AI agents from lying about completed work?
It seals finished work into a ProofPacket where every artifact is hashed and the packet is HMAC-signed, allowing for verifiable re-checks.
Can rigforge catch forged build claims?
Yes, it is designed to catch forged claims; benchmarks show it caught 8/8 forgeries with 1.00 accuracy in tested scenarios.
Is the signing key shared with the AI agent?
No, the signing key stays with the user and is never shared with the agent.
What is the security limitation of the HMAC signatures?
HMAC signatures are symmetric, which limits who can verify the packets.