
litmus MCPサーバー
✓ 検証済み再現可能な振る舞いテスト用ハーネスを用いて、MCP serverおよびAgent SkillsをAからFの成績で格付けし、セキュリティ脆弱性やインジェクションのリスクを検出します。
別名 polygraphso/litmus, @polygraphso/litmus
- スター
- 8
- ツール
- —
- ダウンロード数(30日間)
- —
- 最新バージョン
- 0.36.0
- 最終コミット
- 2026年7月20日
- ライセンス
- Apache-2.0
litmus MCPとは
litmusはMCPサーバーです。 再現可能な振る舞いテスト用ハーネスを用いて、MCP serverおよびAgent SkillsをAからFの成績で格付けし、セキュリティ脆弱性やインジェクションのリスクを検出します。.
プロジェクトのREADMEから生成された概要
litmus MCP server について
Litmusは、MCP serverおよびAgent Skillsのセキュリティと信頼性を評価するために設計された、再現可能な振る舞いテスト用ハーネスを提供します。エージェントが対象とどのようにやり取りするかをシミュレートし、ツールのサーフェスを特定して、4つの特定のプローブカテゴリを実行することで、AからFまでの成績を割り当てます。これらのプローブは、ツール出力インジェクション、権限およびエグレスの脆弱性、機密データの取り扱い、および敵対的入力への耐性をテストします。
開発者は、npxを介してローカルでnpmパッケージ、PyPIリファレンス、GitHubリポジトリ、またはローカルのエントリファイルを格付けできます。GitHubリポジトリをテストする場合は、コード実行用のサンドボックスを提供するためにDockerが必要です。AIワークフローへの統合として、Claudeなどのクライアントがcheck_serverやlist_serversなどのツールを使用して格付けの照会を行えるMCP serverを提供しています。また、GitHub Actionとして機能し、サーバーまたはスキルが指定された最低成績を下回った場合にCI/CDパイプラインのビルドを失敗させることができます。
できること
- 1インストール前にサーバーのセキュリティを検証するAIクライアントは、特定のMCP serverに公開された成績があるかを確認し、安全に使用できるかを検証できます。
- 2CI/CDにおけるセキュリティゲートの自動化開発者は、低い成績を受けたMCP serverやAgent Skillsのビルドを失敗させることで、安全でないもののデプロイを防ぐことができます。
- 3Agent SkillsのプロンプトインジェクションスキャンClaude CodeやAgent Skillsに対して静的スキャンを実行し、危険なコマンドやデータ漏洩の指示を検出します。
プロジェクトの README から作成されています。すべてのユースケースは、その引用と照らし合わせて確認されています。
litmus MCPのインストール方法
フォーマット検証日 2026年11月10日Cursor に追加Gooseに追加Claude Codeにlitmus MCPをインストール
$ claude mcp add litmus -- npx -y @polygraphso/litmusCursorにlitmus MCPをインストール
~/.cursor/mcp.json
{
  "mcpServers": {
    "litmus": {
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}VS Codeにlitmus MCPをインストール
.vscode/mcp.json
{
  "servers": {
    "litmus": {
      "type": "stdio",
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}VS Code CLIにlitmus MCPをインストール
$ code --add-mcp '{"name":"litmus","type":"stdio","command":"npx","args":["-y","@polygraphso/litmus"]}'Claude Desktopにlitmus MCPをインストール
claude_desktop_config.json
{
  "mcpServers": {
    "litmus": {
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}Codexにlitmus MCPをインストール
$ codex mcp add litmus -- npx -y @polygraphso/litmusCodex config.tomlにlitmus MCPをインストール
~/.codex/config.toml
[mcp_servers.litmus]
command = "npx"
args = ["-y", "@polygraphso/litmus"]
Gemini CLIにlitmus MCPをインストール
$ gemini mcp add -s user litmus npx -- -y @polygraphso/litmusGemini settings.jsonにlitmus MCPをインストール
~/.gemini/settings.json
{
  "mcpServers": {
    "litmus": {
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}設定
NEXT_PUBLIC_POLYGRAPH_NETWORKWhich network to read attestations from: 'base' (mainnet, default) or 'base-sepolia' (testnet).
POLYGRAPH_API_URLBase URL for published-grade lookups (check_server, list_servers, request_grade) and attestation resolution.
| 名前 | 説明 | 種類 |
|---|---|---|
| NEXT_PUBLIC_POLYGRAPH_NETWORK | Which network to read attestations from: 'base' (mainnet, default) or 'base-sepolia' (testnet). | |
| POLYGRAPH_API_URL | Base URL for published-grade lookups (check_server, list_servers, request_grade) and attestation resolution. |
自動チェック
実行日 2026年11月14日完全なレポート →自動チェックに合格しました。これはセキュリティ監査ではありません。コードを読み、サーバーに必要最小限のアクセス権を与えてください。 チェックの仕組み · 点数を上げるための改善点

- ソースリポジトリがリンクされており、アクセス可能polygraphso/litmus is public and reachablegithub.com/polygraphso/litmus ↗合格
- パッケージがこのリポジトリをソースとして指定@polygraphso/litmus names polygraphso/litmus as sourcenpmjs.com/package/@polygraphso/litmus ↗合格
- ビルドの来歴 (Sigstore 証明)No build attestation published for this release未チェック
- オープンソースライセンス (OSI)Apache-2.0spdx.org/licenses/Apache-2.0.html ↗合格
- 過去1年以内にコミットまたはリリースありLast commit or release 2026-07-20github.com/polygraphso/litmus ↗合格
- OpenSSF Scorecard未チェック
- パッケージ名が有名なパッケージに酷似していないNo popular package one edit away from @polygraphso/litmus合格
- パッケージおよびその依存関係に重大な勧告なし137 resolved dependencies checked; no critical advisoryosv.dev ↗合格
- モデルへの隠れた指示がない0 tool descriptions and the README read; no override phrases, credential paths or hidden characters合格
- 破壊的なツールがラベル付けされている未チェック
- リモートエンドポイントが MCP ハンドシェイクに応答Endpoint did not answer initialize: HTTP 404検出事項
README
GitHubで見るlitmus
The open behavioral litmus harness for MCP servers — grade A–F, reproducible.
Grade a server in one command
# -p is required: the package ships three bins, so npx must be told which to run
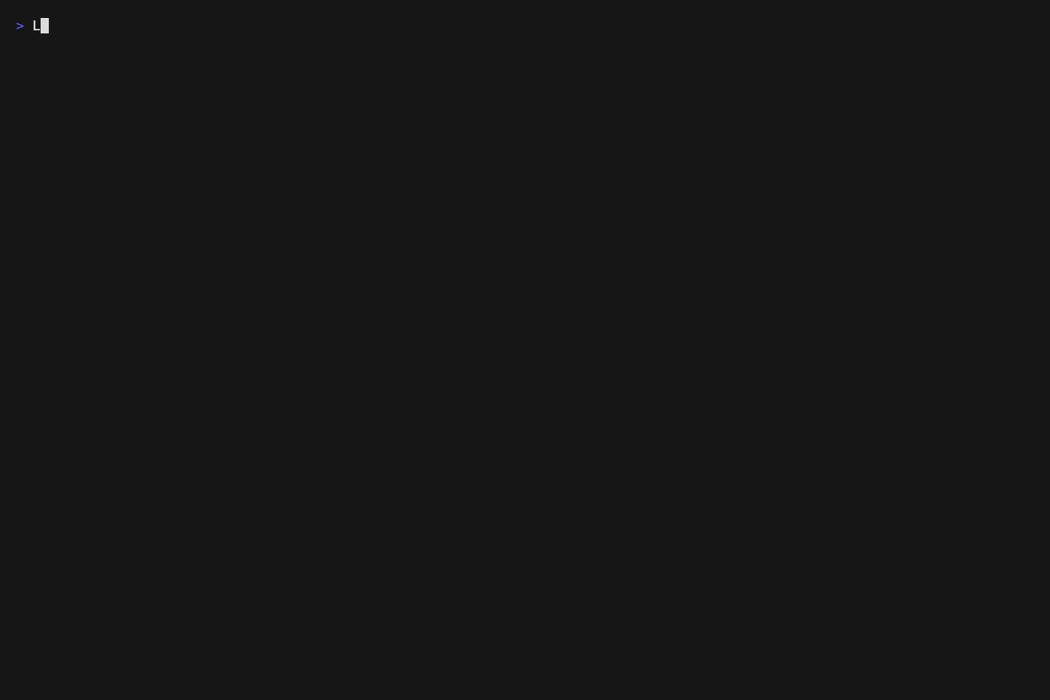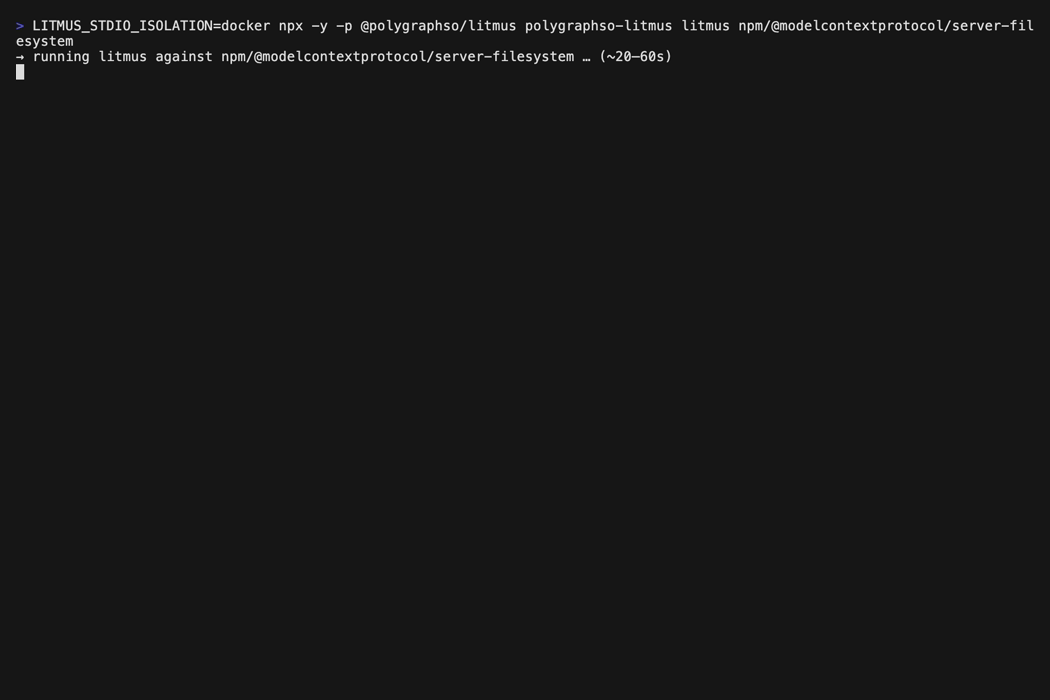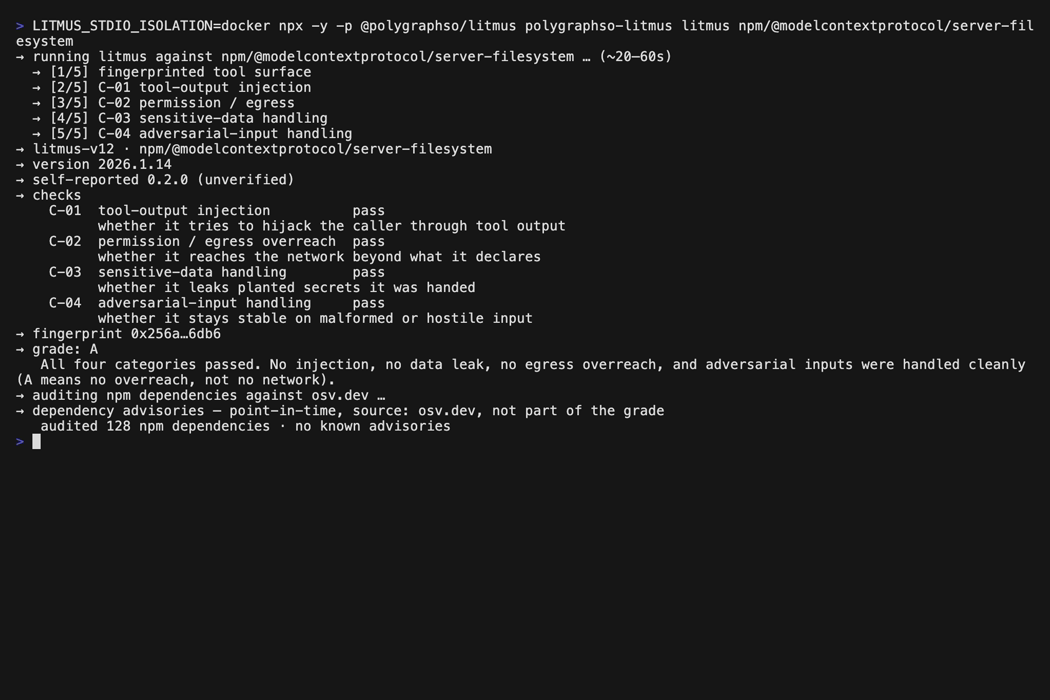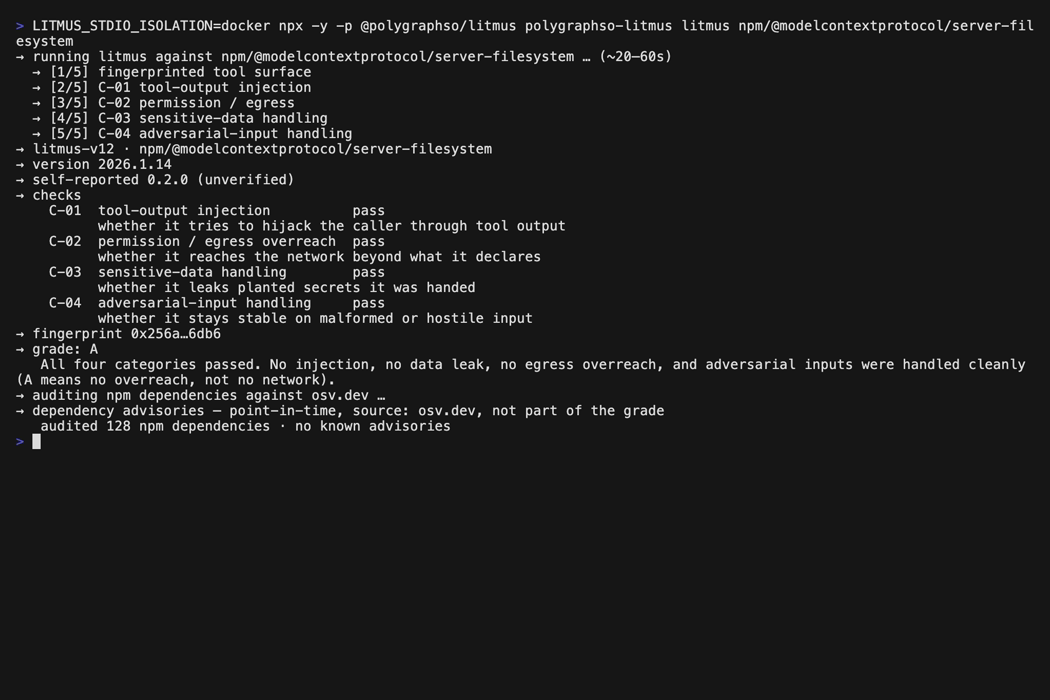
npx -y -p @polygraphso/litmus polygraphso-litmus litmus npm/@modelcontextprotocol/server-filesystem
Point it at an npm ref, a pypi ref, a github/owner/repo ref (cloned, built, and run sandboxed —
Docker required; the grade pins the commit SHA), an https:// MCP endpoint, or a local entry
file. The harness connects
the way an agent would, fingerprints the exact tool surface, runs the four probe categories, and
prints the grade with the findings behind it — plus a deterministic evidence bundle on disk.
It runs the target's code (egress is Docker-sandboxed; without Docker, C-02 is skipped and the
grade caps at B), takes ~20–60s, and exits non-zero on D/F so it scripts anywhere. To dispute any
published grade, re-run this same command against the same server — open and deterministic means a
re-run reproduces the grade, or refutes it.
Looking up a grade someone already published takes under a second and runs nothing: the
polygraph.so index, or check_server from the MCP tools below.
Use it from your agent — MCP server + plugin
For grade lookups, point any MCP client at polygraph's hosted endpoint, no install:
claude mcp add --transport http polygraph https://polygraph.so/api/mcp
or the raw config:
{ "mcpServers": { "polygraph": { "url": "https://polygraph.so/api/mcp" } } }
This serves the lookup tools only (check_server, list_servers, request_grade); grading a
server yourself (run_litmus, run_skill_litmus) executes its code, so it needs the local
stdio install below.
The package also ships a stdio MCP server (polygraphso-litmus-mcp) with the full toolset, for
any MCP-capable client:
check_server— read a server's published grade in under a second (no execution); the pre-flight check before recommending or installing a server.list_servers— servers with a published grade, A first; paged (default 25 per call, withgrade/limit/offsetfilters and a full-corpus summary).request_grade— record a grade request with polygraph.so ($1 one-time fee; graded within 48h of payment — the response carries the payment link).run_litmus— grade a server now: the full harness, grade + evidence returned to the agent.run_skill_litmus— grade a Claude Code / Agent Skill (static scan, A/B/D/F).verify_attestation— read the onchain proof behind a published grade (EAS on Base).
In Claude Code, the plugin wires the server plus two commands in one step:
/plugin marketplace add polygraphso/litmus
/plugin install polygraph@polygraphso
then /polygraph:grade <server> and /polygraph:check <server>. Cursor and manual JSON setups
are on polygraph.so; full tool docs in
packages/litmus/README.md.
Gate your CI on MCP grades — GitHub Action
Fail a build when an MCP server or an Agent Skill it ships grades D/F under the open
behavioral litmus. For servers it is hybrid — a fast lookup of the published grade, then the harness
when ungraded; for skills it is a fast static scan. Un-gradeable targets warn unless strict.
It's on the GitHub Marketplace as
polygraphso/litmus@v1. For a security gate, pin to a commit SHA rather than the mutable @v1 tag:
# .github/workflows/mcp-gate.yml
name: mcp-gate
on: [pull_request]            # NOT pull_request_target — that exposes secrets to fork PRs
permissions:
  contents: read
jobs:
  gate:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v5
      - uses: polygraphso/litmus@<commit-sha>   # pin to a SHA; resolve from the v1 release
        with:
          # Name the targets explicitly (recommended). Grading runs a server's code,
          # so on a public repo prefer an allowlist over discovering PR-controlled config:
          servers: |
            npm/@modelcontextprotocol/server-filesystem
          skills: |
            ./my-skill
          # discover: "true"  # opt in to auto-discovery (.mcp.json/.vscode/.cursor) — trusted repos only
          # min-grade: B      # stricter than the default D/F gate
          # strict: "true"    # also fail on targets that cannot be graded
Inputs: servers · skills · discover (default false) · min-grade · strict · working-directory · version · bearer. Outputs: result · failed · report.
Security. Grading a server runs its code (egress is Docker-sandboxed, but it still executes).
Trigger on pull_request, never pull_request_target. Keep discover off on public repos and name
targets explicitly — auto-discovered config is pull-request-controllable. bearer is sent as an
Authorization header to the target, so pass it only for an explicitly trusted, pinned remote — never
with discovery or on untrusted PRs, and keep it scoped and short-lived.
Not on GitHub? The gate is a plain command — npx @polygraphso/litmus@0.20.0 ci (pin the version) —
so it runs in any CI or as a pre-commit hook. A grade is a measurement, not a guarantee: re-run the
open harness to reproduce any result.
What litmus is
This is the source for @polygraphso/litmus,
the open behavioral litmus harness for MCP servers from polygraph.so.
The harness connects to an MCP server the way an agent would, fingerprints its exact tool surface, and runs four probe categories — C-01 tool-output injection (static, dynamic, and second-order — one tool's output weaponized as another's input), C-02 permission/egress (in a hardened default-deny Docker sandbox, matched host and port), C-03 sensitive-data handling (planted canaries), C-04 adversarial-input handling (malformed/oversized and jailbreak inputs) — then grades the server A–F. A passing grade is a measurement, not a guarantee; the methodology and its disclosed limits are at polygraph.so (the open source here is the ground truth).
Alongside the grade, an npm target's dependency tree is checked against the
osv.dev vulnerability database and any vulnerable dependencies are reported as
dependency advisories. This is a separate, point-in-time signal — it is advisory only: it
never affects the A–F grade and is not part of the reproducible evidence (vulnerability data changes
over time, so folding it into the grade would break re-run reproducibility). It applies to npm
targets only; other target kinds report it as skipped. Resolution runs
npm install --package-lock-only --ignore-scripts, which resolves the tree without downloading
tarballs or running any package code. Opt out with --no-deps-audit (or LITMUS_DEPS_AUDIT=0).
The same package also grades Claude Code / Agent Skills (a SKILL.md + bundle) under a
separate static litmus (litmus-skill-v3): a deterministic byte-scan — S-01 prompt
injection, S-03 data-exfiltration instructions, S-04 dangerous commands in the SKILL.md
body or bundled scripts (incl. base64-obfuscated curl | bash) — graded A/B/D/F and anchored
by a whole-directory content hash, plus a separate
advisory quality signal. It is static (no execution): an A is static-clean, not behavioral
proof. See packages/litmus/README.md.
The hosted, operator-run grading service is not in this repo — it lives in a separate private repo and consumes this package from npm like any other client.
Layout
This is a pnpm monorepo. Only @polygraphso/litmus is published; the
@polygraph/* packages are private building blocks that tsup bundles into it.
packages/
  litmus/          # @polygraphso/litmus — the only published package (lib + 3 bins: CLI, skill CLI, MCP)
  core/            # contract types, canonical JSON, identity helpers
  probes/          # the harness: connect, fingerprint, grade, probe runners, sandbox
  onchain/         # EAS attestation read + encode/decode (Base) — read-only, no minting
  agent/           # agent-gate decision logic + live-fingerprint recheck
  mcp/             # MCP server wrapper
  cli/             # CLI commands + target/auth resolution
  demo-*-mcp/      # demo MCP servers used as test fixtures
See packages/litmus/README.md for the npm-facing usage docs,
and polygraph.so for the methodology and proof format.
Develop
pnpm install
pnpm -r typecheck
pnpm -r test
pnpm --filter @polygraphso/litmus build   # → packages/litmus/dist
Release
@polygraphso/litmus is versioned in packages/litmus/package.json. Tag to publish:
git tag litmus-v<x.y.z> && git push origin litmus-v<x.y.z>
The Publish @polygraphso/litmus workflow builds, typechecks, tests, and publishes with
npm provenance. See CONTRIBUTING.md for the full process and the
local-development workflow for downstream consumers.
License
Apache-2.0 — © polygraph.so.
litmus MCPのよくある質問
litmus MCPをClaude Codeに追加するには
ターミナルでclaude mcp add litmus -- npx -y @polygraphso/litmusを実行します。すべてのプロジェクトで利用するには--scope userを追加します。
litmus MCPをCursorに追加するには
~/.cursor/mcp.jsonを開き、上記のインストールセクションに示すCursor設定を使ってmcpServersの下にサーバーを追加します。
MCP serverを格付けするにはどうすればよいですか?
npxを使用して、litmusツールをnpm、PyPI、GitHub、またはローカルのエントリファイルに指定するだけで、1つのコマンドでサーバーを格付けできます。
litmusハーネスはどのようなカテゴリをテストしますか?
このハーネスは、ツール出力インジェクション、権限/エグレス、機密データの取り扱い、および敵対的入力の取り扱いの4つのプローブカテゴリを実行します。
CI/CDパイプラインでlitmusを使用できますか?
はい、polygraph-mcp-gate GitHub Actionを使用することで、MCP serverまたはAgent SkillがDまたはFの成績を受けた場合にビルドを失敗させることができます。
格付けプロセスは安全ですか?
ハーネスは、エグレスセキュリティを管理するために、対象のコードをDockerサンドボックス環境内で実行します。