
litmus MCP server
✓ VerifiziertBewertet MCP server und Agent Skills von A bis F mithilfe eines reproduzierbaren Behavioral Harness, um Sicherheitslücken und Injection-Risiken zu erkennen.
Auch bekannt als polygraphso/litmus, @polygraphso/litmus
- Stars
- 8
- Tools
- —
- Downloads, 30 Tage
- —
- Neueste Version
- 0.36.0
- Letzter Commit
- 20. Juli 2026
- Lizenz
- Apache-2.0
Was ist litmus MCP?
litmus ist ein MCP server. Bewertet MCP server und Agent Skills von A bis F mithilfe eines reproduzierbaren Behavioral Harness, um Sicherheitslücken und Injection-Risiken zu erkennen.
Zusammenfassung generiert aus dem README des Projekts
Über litmus MCP server
Litmus bietet ein reproduzierbares Behavioral Harness, das entwickelt wurde, um die Sicherheit und Zuverlässigkeit von MCP servern und Agent Skills zu bewerten. Es vergibt Noten von A bis F, indem es simuliert, wie ein Agent mit einem Target interagiert, dessen Tool-Surface fingerprintet und vier spezifische Probe-Kategorien ausführt. Diese Probes testen auf Tool-Output Injection, Permission- und Egress-Schwachstellen, den Umgang mit sensiblen Daten sowie die Widerstandsfähigkeit gegen Adversarial Input.
Entwickler können das Tool lokal via npx nutzen, um npm-Packages, PyPI-Referenzen, GitHub-Repositories oder lokale Entry-Files zu bewerten. Beim Testen von GitHub-Repositories ist Docker erforderlich, um eine Sandbox für die Code-Ausführung bereitzustellen. Für die Integration in AI-Workflows bietet es einen MCP server an, der es Clients wie Claude ermöglicht, Noten über Tools wie check_server und list_servers abzufragen. Zudem fungiert es als GitHub Action, um CI/CD-Pipelines zu kontrollieren und Builds fehlschlagen zu lassen, falls ein Server oder Skill unter eine festgelegte Mindestnote fällt.
Was du damit machen kannst
- 1Server-Sicherheit vor der Installation prüfenEin AI-Client kann prüfen, ob ein spezifischer MCP server eine veröffentlichte Note hat, um sicherzustellen, dass die Nutzung sicher ist.
- 2Security Gates in CI/CD automatisierenEntwickler können verhindern, dass unsichere MCP server oder Agent Skills deployed werden, indem sie Builds mit schlechten Noten blockieren.
- 3Agent Skills auf Prompt Injection scannenFühre einen Scan auf Claude Code oder Agent Skills durch, um gefährliche Commands oder Anweisungen zur Datenexfiltration zu entdecken.
Geschrieben aus dem README des Projekts. Jeder Use Case wurde gegen ein Zitat daraus geprüft.
So installierst du litmus MCP
Formate geprüft am 10. Nov. 2026Zu Cursor hinzufügenZu Goose hinzufügenlitmus MCP in Claude Code installieren
$ claude mcp add litmus -- npx -y @polygraphso/litmuslitmus MCP in Cursor installieren
~/.cursor/mcp.json
{
  "mcpServers": {
    "litmus": {
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}litmus MCP in VS Code installieren
.vscode/mcp.json
{
  "servers": {
    "litmus": {
      "type": "stdio",
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}litmus MCP in VS Code CLI installieren
$ code --add-mcp '{"name":"litmus","type":"stdio","command":"npx","args":["-y","@polygraphso/litmus"]}'litmus MCP in Claude Desktop installieren
claude_desktop_config.json
{
  "mcpServers": {
    "litmus": {
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}litmus MCP in Codex installieren
$ codex mcp add litmus -- npx -y @polygraphso/litmuslitmus MCP in Codex config.toml installieren
~/.codex/config.toml
[mcp_servers.litmus]
command = "npx"
args = ["-y", "@polygraphso/litmus"]
litmus MCP in Gemini CLI installieren
$ gemini mcp add -s user litmus npx -- -y @polygraphso/litmuslitmus MCP in Gemini settings.json installieren
~/.gemini/settings.json
{
  "mcpServers": {
    "litmus": {
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}Konfiguration
NEXT_PUBLIC_POLYGRAPH_NETWORKWhich network to read attestations from: 'base' (mainnet, default) or 'base-sepolia' (testnet).
POLYGRAPH_API_URLBase URL for published-grade lookups (check_server, list_servers, request_grade) and attestation resolution.
| Name | Beschreibung | Typ |
|---|---|---|
| NEXT_PUBLIC_POLYGRAPH_NETWORK | Which network to read attestations from: 'base' (mainnet, default) or 'base-sepolia' (testnet). | |
| POLYGRAPH_API_URL | Base URL for published-grade lookups (check_server, list_servers, request_grade) and attestation resolution. |
Automatisierte Checks
Geluften am 14. Nov. 2026Vollständiger Bericht →Unsere automatisierten Checks bestanden. Das ist kein Security-Audit: Lies den Code und gib dem Server nur den minimal notwendigen Zugriff. Wie die Checks funktionieren · Was du für mehr Punkte verbessern kannst

- Source Repository verknüpft und erreichbarpolygraphso/litmus is public and reachablegithub.com/polygraphso/litmus ↗Bestanden
- Paket nennt dieses Repository als Quelle@polygraphso/litmus names polygraphso/litmus as sourcenpmjs.com/package/@polygraphso/litmus ↗Bestanden
- Build-Provenienz (Sigstore-Attestierung)No build attestation published for this releaseNicht geprüft
- Open Source Lizenz (OSI)Apache-2.0spdx.org/licenses/Apache-2.0.html ↗Bestanden
- Commit oder Release im letzten JahrLast commit or release 2026-07-20github.com/polygraphso/litmus ↗Bestanden
- OpenSSF ScorecardNicht geprüft
- Package-Name ähnelt keinem populären PackageNo popular package one edit away from @polygraphso/litmusBestanden
- Keine kritischen Advisories im Paket oder seinen Abhängigkeiten137 resolved dependencies checked; no critical advisoryosv.dev ↗Bestanden
- Keine versteckten Anweisungen an das Modell0 tool descriptions and the README read; no override phrases, credential paths or hidden charactersBestanden
- Destruktive Tools sind markiertNicht geprüft
- Remote-Endpoint beantwortet den MCP-HandshakeEndpoint did not answer initialize: HTTP 404Befund
README
Auf GitHub ansehenlitmus
The open behavioral litmus harness for MCP servers — grade A–F, reproducible.
Grade a server in one command
# -p is required: the package ships three bins, so npx must be told which to run
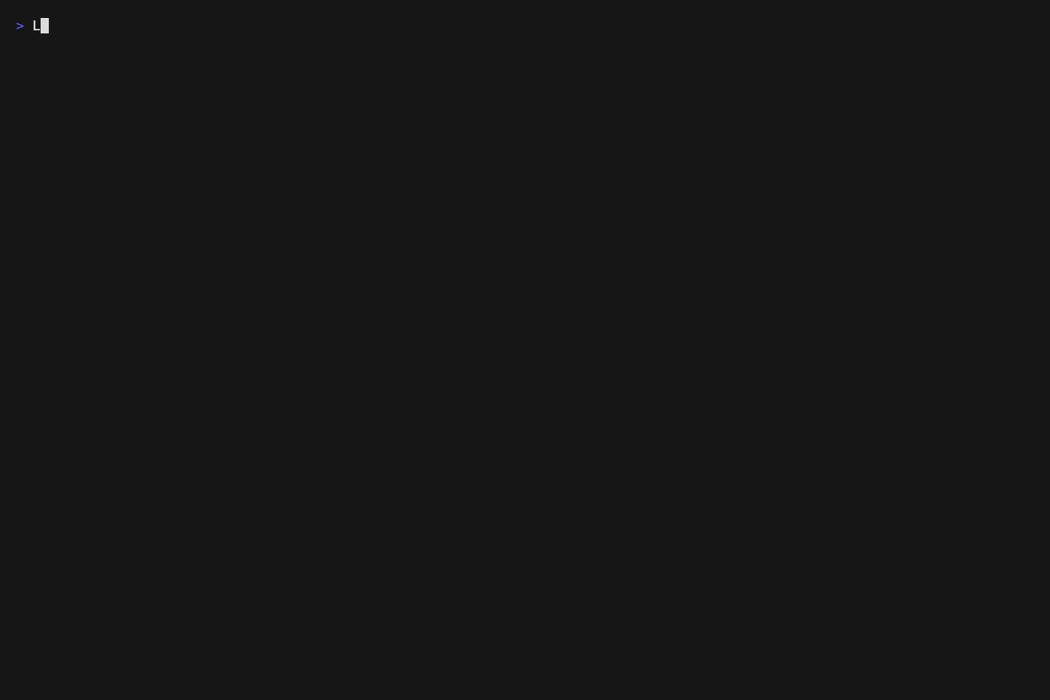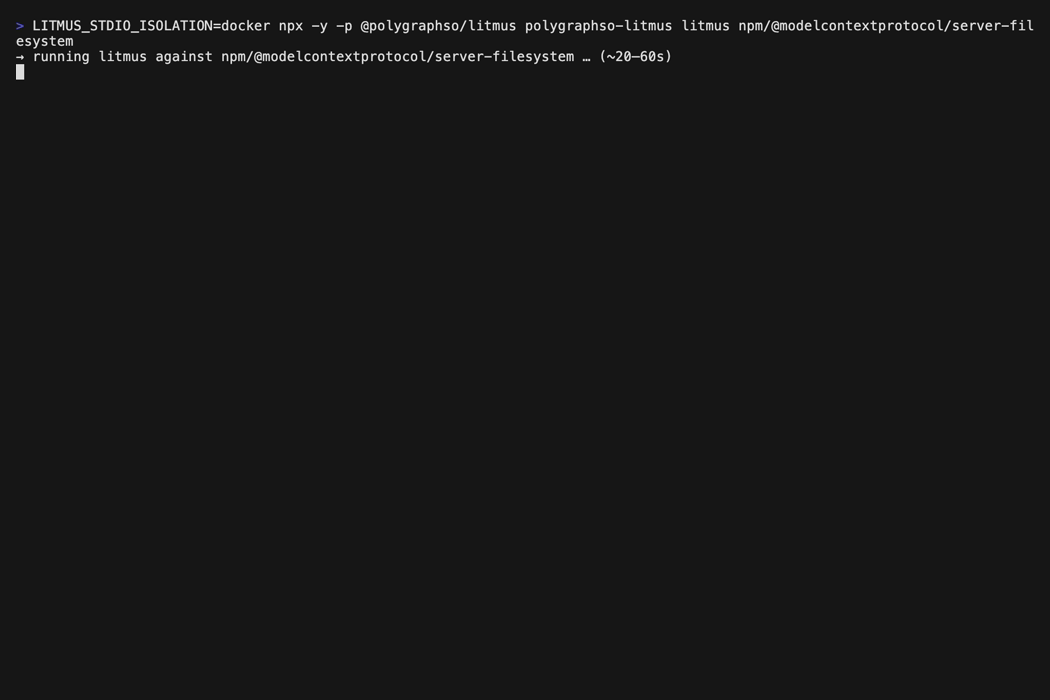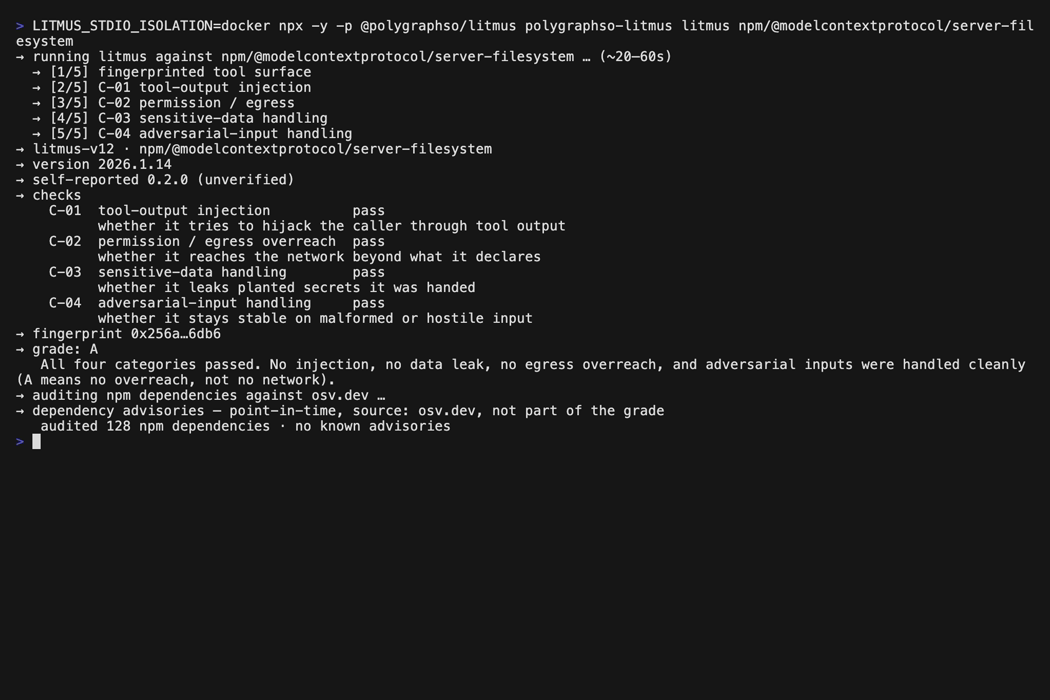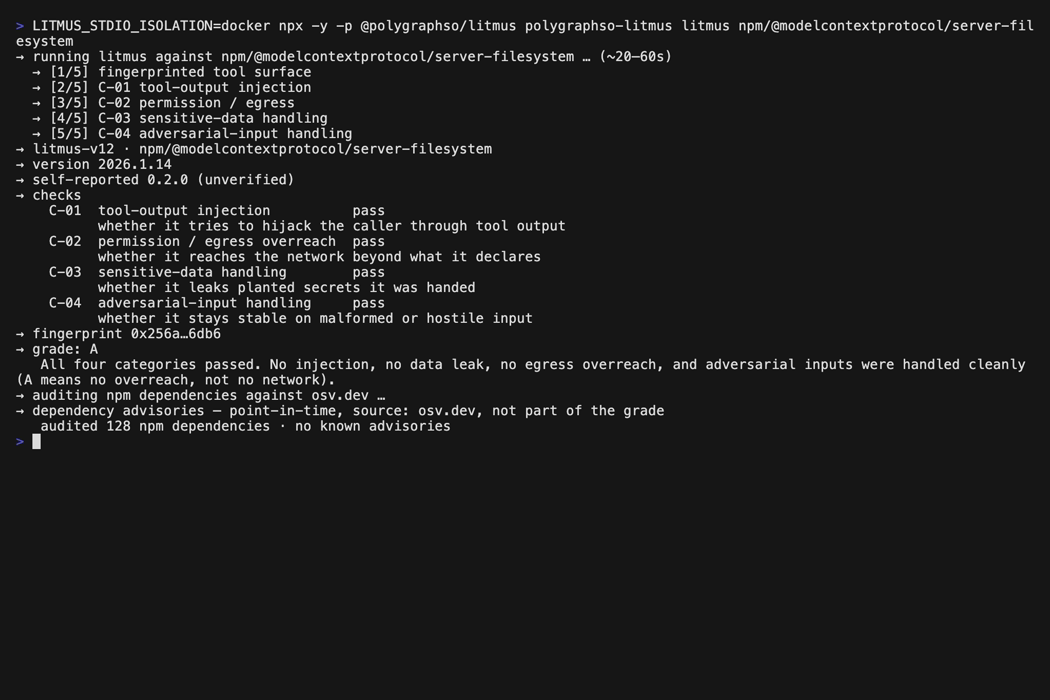
npx -y -p @polygraphso/litmus polygraphso-litmus litmus npm/@modelcontextprotocol/server-filesystem
Point it at an npm ref, a pypi ref, a github/owner/repo ref (cloned, built, and run sandboxed —
Docker required; the grade pins the commit SHA), an https:// MCP endpoint, or a local entry
file. The harness connects
the way an agent would, fingerprints the exact tool surface, runs the four probe categories, and
prints the grade with the findings behind it — plus a deterministic evidence bundle on disk.
It runs the target's code (egress is Docker-sandboxed; without Docker, C-02 is skipped and the
grade caps at B), takes ~20–60s, and exits non-zero on D/F so it scripts anywhere. To dispute any
published grade, re-run this same command against the same server — open and deterministic means a
re-run reproduces the grade, or refutes it.
Looking up a grade someone already published takes under a second and runs nothing: the
polygraph.so index, or check_server from the MCP tools below.
Use it from your agent — MCP server + plugin
For grade lookups, point any MCP client at polygraph's hosted endpoint, no install:
claude mcp add --transport http polygraph https://polygraph.so/api/mcp
or the raw config:
{ "mcpServers": { "polygraph": { "url": "https://polygraph.so/api/mcp" } } }
This serves the lookup tools only (check_server, list_servers, request_grade); grading a
server yourself (run_litmus, run_skill_litmus) executes its code, so it needs the local
stdio install below.
The package also ships a stdio MCP server (polygraphso-litmus-mcp) with the full toolset, for
any MCP-capable client:
check_server— read a server's published grade in under a second (no execution); the pre-flight check before recommending or installing a server.list_servers— servers with a published grade, A first; paged (default 25 per call, withgrade/limit/offsetfilters and a full-corpus summary).request_grade— record a grade request with polygraph.so ($1 one-time fee; graded within 48h of payment — the response carries the payment link).run_litmus— grade a server now: the full harness, grade + evidence returned to the agent.run_skill_litmus— grade a Claude Code / Agent Skill (static scan, A/B/D/F).verify_attestation— read the onchain proof behind a published grade (EAS on Base).
In Claude Code, the plugin wires the server plus two commands in one step:
/plugin marketplace add polygraphso/litmus
/plugin install polygraph@polygraphso
then /polygraph:grade <server> and /polygraph:check <server>. Cursor and manual JSON setups
are on polygraph.so; full tool docs in
packages/litmus/README.md.
Gate your CI on MCP grades — GitHub Action
Fail a build when an MCP server or an Agent Skill it ships grades D/F under the open
behavioral litmus. For servers it is hybrid — a fast lookup of the published grade, then the harness
when ungraded; for skills it is a fast static scan. Un-gradeable targets warn unless strict.
It's on the GitHub Marketplace as
polygraphso/litmus@v1. For a security gate, pin to a commit SHA rather than the mutable @v1 tag:
# .github/workflows/mcp-gate.yml
name: mcp-gate
on: [pull_request]            # NOT pull_request_target — that exposes secrets to fork PRs
permissions:
  contents: read
jobs:
  gate:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v5
      - uses: polygraphso/litmus@<commit-sha>   # pin to a SHA; resolve from the v1 release
        with:
          # Name the targets explicitly (recommended). Grading runs a server's code,
          # so on a public repo prefer an allowlist over discovering PR-controlled config:
          servers: |
            npm/@modelcontextprotocol/server-filesystem
          skills: |
            ./my-skill
          # discover: "true"  # opt in to auto-discovery (.mcp.json/.vscode/.cursor) — trusted repos only
          # min-grade: B      # stricter than the default D/F gate
          # strict: "true"    # also fail on targets that cannot be graded
Inputs: servers · skills · discover (default false) · min-grade · strict · working-directory · version · bearer. Outputs: result · failed · report.
Security. Grading a server runs its code (egress is Docker-sandboxed, but it still executes).
Trigger on pull_request, never pull_request_target. Keep discover off on public repos and name
targets explicitly — auto-discovered config is pull-request-controllable. bearer is sent as an
Authorization header to the target, so pass it only for an explicitly trusted, pinned remote — never
with discovery or on untrusted PRs, and keep it scoped and short-lived.
Not on GitHub? The gate is a plain command — npx @polygraphso/litmus@0.20.0 ci (pin the version) —
so it runs in any CI or as a pre-commit hook. A grade is a measurement, not a guarantee: re-run the
open harness to reproduce any result.
What litmus is
This is the source for @polygraphso/litmus,
the open behavioral litmus harness for MCP servers from polygraph.so.
The harness connects to an MCP server the way an agent would, fingerprints its exact tool surface, and runs four probe categories — C-01 tool-output injection (static, dynamic, and second-order — one tool's output weaponized as another's input), C-02 permission/egress (in a hardened default-deny Docker sandbox, matched host and port), C-03 sensitive-data handling (planted canaries), C-04 adversarial-input handling (malformed/oversized and jailbreak inputs) — then grades the server A–F. A passing grade is a measurement, not a guarantee; the methodology and its disclosed limits are at polygraph.so (the open source here is the ground truth).
Alongside the grade, an npm target's dependency tree is checked against the
osv.dev vulnerability database and any vulnerable dependencies are reported as
dependency advisories. This is a separate, point-in-time signal — it is advisory only: it
never affects the A–F grade and is not part of the reproducible evidence (vulnerability data changes
over time, so folding it into the grade would break re-run reproducibility). It applies to npm
targets only; other target kinds report it as skipped. Resolution runs
npm install --package-lock-only --ignore-scripts, which resolves the tree without downloading
tarballs or running any package code. Opt out with --no-deps-audit (or LITMUS_DEPS_AUDIT=0).
The same package also grades Claude Code / Agent Skills (a SKILL.md + bundle) under a
separate static litmus (litmus-skill-v3): a deterministic byte-scan — S-01 prompt
injection, S-03 data-exfiltration instructions, S-04 dangerous commands in the SKILL.md
body or bundled scripts (incl. base64-obfuscated curl | bash) — graded A/B/D/F and anchored
by a whole-directory content hash, plus a separate
advisory quality signal. It is static (no execution): an A is static-clean, not behavioral
proof. See packages/litmus/README.md.
The hosted, operator-run grading service is not in this repo — it lives in a separate private repo and consumes this package from npm like any other client.
Layout
This is a pnpm monorepo. Only @polygraphso/litmus is published; the
@polygraph/* packages are private building blocks that tsup bundles into it.
packages/
  litmus/          # @polygraphso/litmus — the only published package (lib + 3 bins: CLI, skill CLI, MCP)
  core/            # contract types, canonical JSON, identity helpers
  probes/          # the harness: connect, fingerprint, grade, probe runners, sandbox
  onchain/         # EAS attestation read + encode/decode (Base) — read-only, no minting
  agent/           # agent-gate decision logic + live-fingerprint recheck
  mcp/             # MCP server wrapper
  cli/             # CLI commands + target/auth resolution
  demo-*-mcp/      # demo MCP servers used as test fixtures
See packages/litmus/README.md for the npm-facing usage docs,
and polygraph.so for the methodology and proof format.
Develop
pnpm install
pnpm -r typecheck
pnpm -r test
pnpm --filter @polygraphso/litmus build   # → packages/litmus/dist
Release
@polygraphso/litmus is versioned in packages/litmus/package.json. Tag to publish:
git tag litmus-v<x.y.z> && git push origin litmus-v<x.y.z>
The Publish @polygraphso/litmus workflow builds, typechecks, tests, and publishes with
npm provenance. See CONTRIBUTING.md for the full process and the
local-development workflow for downstream consumers.
License
Apache-2.0 — © polygraph.so.
litmus MCP Fragen
Wie füge ich litmus MCP zu Claude Code hinzu?
Führe claude mcp add litmus -- npx -y @polygraphso/litmus in deinem Terminal aus. Füge --scope user hinzu, damit der Server in jedem Projekt verfügbar ist.
Wie füge ich litmus MCP zu Cursor hinzu?
Öffne ~/.cursor/mcp.json und füge den Server unter mcpServers hinzu, mit der Cursor-Config aus dem Installationsabschnitt oben.
Wie bewerte ich einen MCP server?
Du kannst einen Server mit einem einzigen Befehl via npx bewerten, indem du das litmus-Tool auf eine npm-, PyPI-, GitHub- oder lokale Entry-Datei richtest.
Welche Kategorien testet das litmus harness?
Das Harness führt vier Probe-Kategorien aus: Tool-Output Injection, Permission/Egress, Sensitive-Data Handling und Adversarial-Input Handling.
Kann ich litmus in meiner CI/CD-Pipeline nutzen?
Ja, du kannst die polygraph-mcp-gate GitHub Action verwenden, um Builds fehlschlagen zu lassen, wenn ein MCP server oder Agent Skill die Note D oder F erhält.
Ist der Bewertungsprozess sicher?
Das Harness führt den Code des Targets innerhalb einer Docker-Sandbox aus, um die Egress-Sicherheit zu gewährleisten.