
AgentAction MCP server
2026년 11월 13일 커밋자율형 AI agent가 결정을 평가하고, 정책을 집행하며, 검증 가능한 증거와 함께 작업을 승인할 수 있도록 신뢰 인프라를 제공합니다.
다른 이름 dinpd/AgentAction
- 스타
- 7
- Tools
- —
- 다운로드, 30일
- —
- 최신 버전
- —
- 마지막 커밋
- 2026년 11월 13일
- 라이선스
- Apache-2.0
AgentAction MCP란?
AgentAction은(는) MCP server입니다. 자율형 AI agent가 결정을 평가하고, 정책을 집행하며, 검증 가능한 증거와 함께 작업을 승인할 수 있도록 신뢰 인프라를 제공합니다.
프로젝트 README에서 생성된 요약
AgentAction MCP server 정보
AgentAction은 의사 결정 평가 및 정책 집행을 위한 신뢰 인프라를 제공하여 기업 환경 내 자율형 AI agent를 보호합니다. 이 시스템은 agent와 시스템 사이의 계층 역할을 수행하며, 작업 승인 및 전체 agent 생애 주기에 걸친 검증 가능한 증거 보존을 담당합니다. 개발자는 모델의 메모리 외부에서 실행되는 런타임 체크를 구현함으로써, 제어되지 않는 도구 루프, 중복 결제 또는 승인되지 않은 데이터 이동과 같은 문제를 방지할 수 있습니다.
사용자는 @dinpd/ai-agent-guard 패키지를 사용하여 프로세스 내 도구 및 흐름 체크를 위한 로컬 TypeScript 가드로 배포하거나, 기존 트래픽을 변경하지 않고 MCP 워크플로우를 검사할 수 있는 Node HTTP sidecar의 observe 모드로 배포할 수 있습니다. 이 시스템은 수동적 MCP observer, Cloudflare Access로 보호되는 호스팅된 운영 콘솔, Hermes agent용 특화 플러그인을 포함한 다양한 통합 패턴을 지원합니다. 범위가 지정된 JIT 권한 및 지속적인 감독 실행을 관리하려면 tenant, source, tool 정책 설정이 필요합니다.
활용 사례
- 1중복 금융 거래 방지상태 유지 idempotency 체크를 통해 AI agent가 동일한 환불이나 결제를 여러 번 실행하는 것을 제한할 수 있습니다.
- 2MCP 워크플로우 동작 모니터링개발자는 수동적 observer를 실행하여 실제 트래픽을 중단하지 않고 특정 정책에 따라 어떤 도구 호출이 허용되거나 거부될지 확인할 수 있습니다.
- 3Human-in-the-loop 승인 강제민감한 작업이 실행되기 전에 정확한 범위에 대한 사람의 승인을 요구하도록 시스템을 구성할 수 있습니다.
- 4DevOps 및 SRE 워크플로우 보안팀은 이 인프라를 사용하여 프로덕션 환경에 대한 배포 승인, canary 모니터링 및 롤백 제어를 관리할 수 있습니다.
프로젝트의 README를 바탕으로 작성되었습니다. 모든 활용 사례는 해당 내용의 인용문과 대조하여 확인합니다.
자동 검사
2026년 11월 15일에 실행됨전체 보고서 →아직 인증되지 않았습니다. 서버는 80점 이상의 점수, 심각한 결함 없음, 그리고 검사에 충분한 데이터를 갖추어야 합니다. 검사 방식 · 점수를 높이기 위해 수정할 항목

- 소스 저장소 연결 및 접근 가능dinpd/agentaction is public and reachablegithub.com/dinpd/agentaction ↗통과
- 패키지가 이 저장소를 소스로 명시검사되지 않음
- 빌드 출처(Sigstore 증명)검사되지 않음
- 오픈 소스 라이선스 (OSI)Apache-2.0spdx.org/licenses/Apache-2.0.html ↗통과
- 최근 1년 내 커밋 또는 릴리스Last commit or release 2026-11-13github.com/dinpd/agentaction ↗통과
- OpenSSF Scorecard검사되지 않음
- 패키지 이름이 인기 패키지와 유사하지 않음검사되지 않음
- 패키지 및 해당 종속성에 중요한 보안 권고 없음검사되지 않음
- 모델에 대한 숨겨진 지침 없음0 tool descriptions and the README read; no override phrases, credential paths or hidden characters통과
- 파괴적인 도구에 라벨 표시됨검사되지 않음
- 원격 엔드포인트가 MCP 핸드셰이크에 응답검사되지 않음
README
GitHub에서 보기AgentAction
Trust infrastructure for autonomous AI agents.
AgentAction is the trust layer between autonomous agents and enterprise systems: it evaluates decisions, enforces policy, authorizes actions, and preserves verifiable evidence across the agent lifecycle. The canonical project site is AgentAction.dev.
AgentAction evaluates decisions, enforces policy, authorizes actions, and preserves verifiable evidence from intent through execution and continuous evaluation.
Intent -> decision assurance -> policy enforcement -> action authorization
       -> execution -> evidence -> continuous evaluation
The action gate is the current enforcement wedge inside that broader trust
lifecycle. Versioned agentpass.* protocol identifiers and the legacy
agentpass and agentid commands remain supported for compatibility. See
Project Positioning for the canonical scope and messaging
boundaries.
Try AgentAction
| Experience | What it demonstrates |
|---|---|
| MCP Readiness Check | Anonymous server inspection, actionable guidance and exportable profiles; opt-in public evidence reused in discovery. |
| Shared authority across providers | Synthetic refund and case closure through separately deployed providers using one authority, distinct signing keys and durable state; challenge eight trust boundaries. |
| Gateway and refund control | Approval, scoped JIT authority, idempotency, audit, and provider-tool authorization in a support workflow. |
| Workato reference integration | A private recipe requests an exact-scope human approval, waits durably, and returns a synthetic refund's signed outcome and frozen intent evidence. |
| n8n reference integration | Native workflows bring automatic or human-reviewed action controls and signed outcome evidence to synthetic refunds. |
| DevOps and SRE control | Production-context checks, deployment approval, JIT grants, dry-run dispatch, canary monitoring, and rollback control. |
| Policy builder | Browser-based manifest authoring with generated YAML, starter OPA policy, and example gateway requests. |
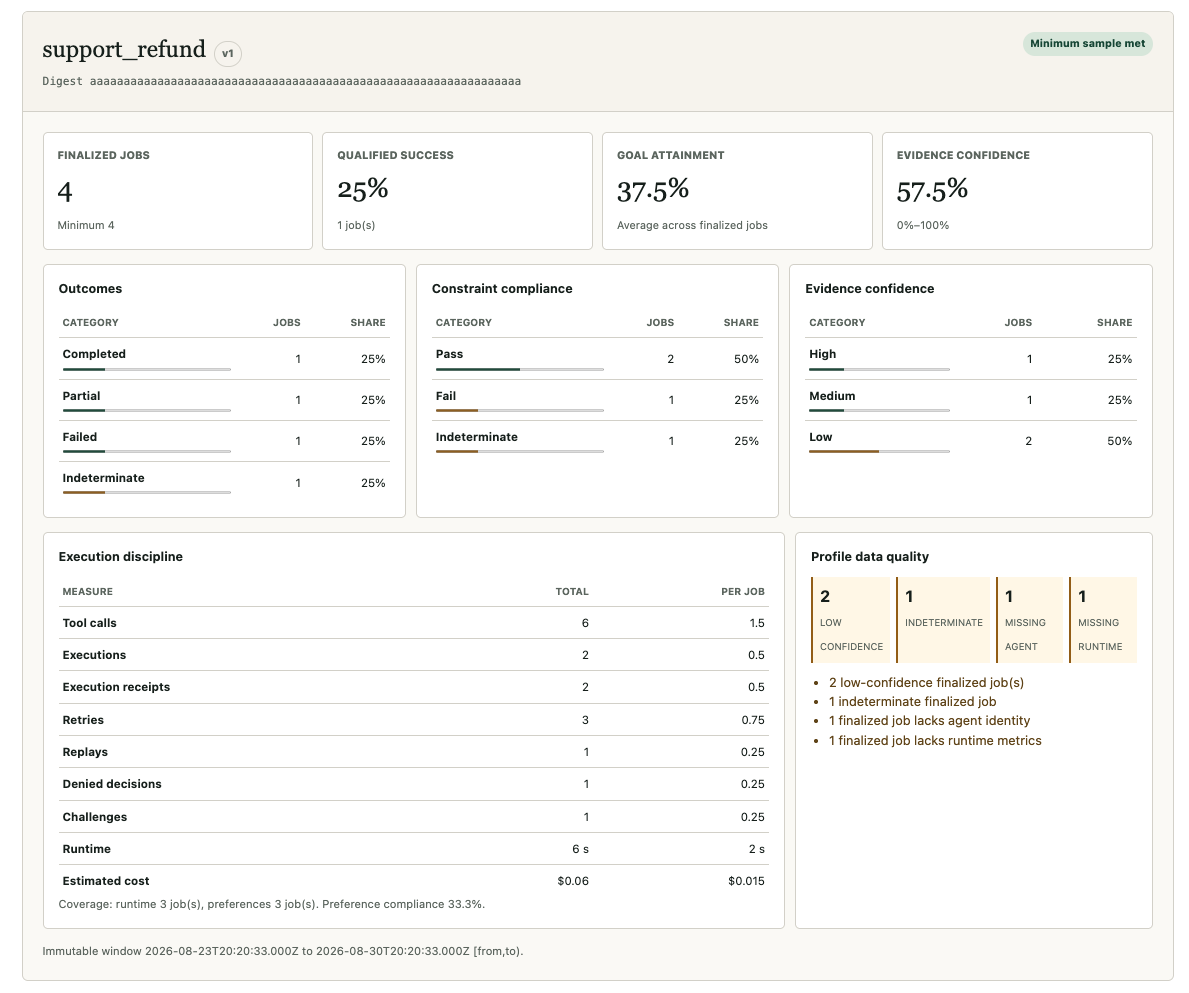
| Observability console demo | Public, read-only Fleet Overview, finalized Jobs explorer, and deterministic evidence timeline backed exclusively by synthetic fixtures. |
| Operator console | Cloudflare Access-protected workspace switching, agent integrations, eval routing, Activity, intent-relative outcomes, constraints, confidence, and evidence. |
In My agents, find MCP servers by capability and review automatic public-information pre-checks before sharing provider credentials. Connect a supported account and create supervised agents with run history. OAuth discovery is available; OAuth login is not yet supported. See pre-check findings and limitations.
Prefer to start without blocking an existing workflow? Run the passive MCP observer quick start below, inspect the counterfactual policy decisions, and enable enforcement only after the boundary matches your intent. Use the public observability demo to inspect the interface without signing in. The separate operator console remains protected by Cloudflare Access. A new identity can create its first workspace; workspace owners can create additional ones and invite viewers or operators by email. Protected invitation links redeem automatically for the exact signed-in email, and every selected workspace is re-authorized server-side before its data is read.
Quick Start
For catalog changes, observed failures and interrupted actions, see MCP workflow diagnostics: compare checker exports locally or in CI, generate a bounded observation report, and run the synthetic recovery walkthrough. These are separate checks; metadata inspection does not prove runtime behavior or a successful business outcome.
Hermes Agent: Native Shadow Observer
Install the repository plugin without adding a proxy or changing Hermes tool execution:
hermes plugins install dinpd/AgentAction/integrations/hermes-agentaction --no-enable
hermes plugins enable agentaction
Configure the hosted endpoint, tenant, source, agent, and tool policies once;
the plugin then exports privacy-safe lifecycle metadata asynchronously. It is
fail open. Hosted setup can explicitly enable bounded agent-declared intent
capture; that adds per-turn model context and two self-attestation tools, and
the console labels the result as untrusted agent provenance. Add both an
explicit intent_id and intent_digest when a run already has an AgentAction
contract; otherwise events are correctly labeled unbound rather than having
intent inferred from prompts or model output.
See the Hermes onboarding guide for the complete flow. The hosted operator console creates a framework-neutral workspace, then provisions a selected Hermes or generic AgentAction source, displays its token once, shows integration-specific connection steps, and verifies the first event. Each Hermes source still uses a separate write-only token whose hash is stored in that tenant's manifest. Workspace owners can then use Evals to create an immutable eval version and route new Jobs by source, agent, or both without changing the Hermes connection.
Test MCP behavior
Enter your server in the MCP checker, review the findings, then Test a tool. Choose staging inputs and Run test in your signed-in workspace; owners and operators can use approved connections without a local install. Save the test to rerun after a fix. Local execution, synthetic examples and file operations are available under More options. The local tester needs one Node 22+ command and no npm install. See setup, saved plans, CI and evidence limits.
Recommended: Observe An MCP Workflow
Run the self-contained observer from a fresh clone:
git clone https://github.com/dinpd/AgentAction.git
cd AgentAction/mcp-gateway-adapter
npm ci
npm run demo:observe
The demo puts the existing reference adapter into passive mode:
MCP client -> customer-run observer adapter -> downstream MCP server
                      |-> local policy + process-local shadow state
                      `-> privacy-safe JSON observation events
Every MCP request and response remains unchanged. The observer records which calls would be allowed, denied, or challenged under enforcement, including stateful findings such as duplicate side effects and tool loops. It does not call hosted authorization, consume approval or JIT authority, filter tool discovery, or attach provider receipts.
The command above is a self-contained onboarding test. To place the adapter in
front of representative traffic, set "mode": "observe", configure its
downstream.url and tool mappings, then start it with:
npx tsx src/index.ts /path/to/observe-config.json
The current deployment is a customer-run Node HTTP sidecar with process-local shadow state and JSON events written to stdout. Review the observe-mode configuration, transition to enforcement, and limitations before using it with a real workflow. The reference adapter is an onboarding and integration surface, not yet a production-complete MCP gateway.
Alternative: Embed The Guard
For an application that owns the tool execution path, install the local TypeScript guard:
npm install @dinpd/ai-agent-guard
Wrap a consequential tool call:
import { createToolGate } from "@dinpd/ai-agent-guard";

const gate = createToolGate({ policy });

const execution = await gate.run(
  {
    agentId: "support-agent",
    jobId: "case-1042",
    tool: "stripe.refund",
    action: "pay",
    resource: "payment/pi_123",
    amountUsd: 49,
    idempotencyKey: "refund-case-1042-pi_123"
  },
  () => stripe.refunds.create({ payment_intent: "pi_123", amount: 4900 })
);

if (!execution.executed) {
  return execution.decision;
}
Run the embedded-guard repository demos:
git clone https://github.com/dinpd/AgentAction.git
cd AgentAction/packages/guard
npm install
npm run demo:quickstart
npm run demo:mcp
npm run demo:circuit
npm run demo:gate
npm run demo:pii
npm test
The guard package is published as
@dinpd/ai-agent-guard.
See packages/guard/ for starter policies and more examples.
Durable supervised execution
Hosted supervised agents use a configurable execution supervisor. Workspace owners set call, approval-lifetime and timeout ceilings; agent and trial limits can narrow them. Exact approvals survive restart, dispatch claims persist before provider calls, and uncertain effects stop for provider review. Inspect action identities and recovery evidence in run history. See the supervisor configuration and guarantees.
How It Works
AgentAction connects six claims without collapsing them together: the declared intent, assessment of the decision, policy authorization, provider execution, independent evidence, and continuous outcome evaluation. Authorization is not proof of execution, and execution is not proof that the intended outcome was achieved within constraints.
Action Authorization
Agent proposes tool call -> AgentAction checks policy + state -> allow / deny / challenge
RBAC can say which identity may access a tool. OAuth can prove access to a server. MCP tool schemas describe inputs. Agent frameworks can decide which tools are visible to a model. AgentAction answers the runtime question:
Should this specific tool call, with this payload, in this job state, execute right now?
The gate runs outside model context and agent-editable memory. It keeps the state needed to stop failures that static access control and prompt rules miss:
- Duplicate refunds, payments, emails, exports, deployments, or writes.
- Runaway loops and repeated tool calls.
- Token, cost, runtime, and tool-call budget spikes.
- PII or sensitive data moving to the wrong destination.
- Risky actions without action-scoped approval.
- Replays or payload changes after authority was granted.
Approvals bind to the proposed tool, resource, payload, amount, destination, job, and expiry. Side-effectful actions bind an idempotency key or call fingerprint to the recorded provider result. The gate therefore remembers what actually executed rather than relying on what the agent thinks happened.
AgentAction separates three concepts that agent systems often blur:
Skill = workflow package
Tool = executable operation
Flow = data movement boundary
The local guard applies tool and flow checks in-process. Larger deployments use the same model through manifests, approvals, hosted gateways, signed receipts, provider-side verification, and durable evidence.
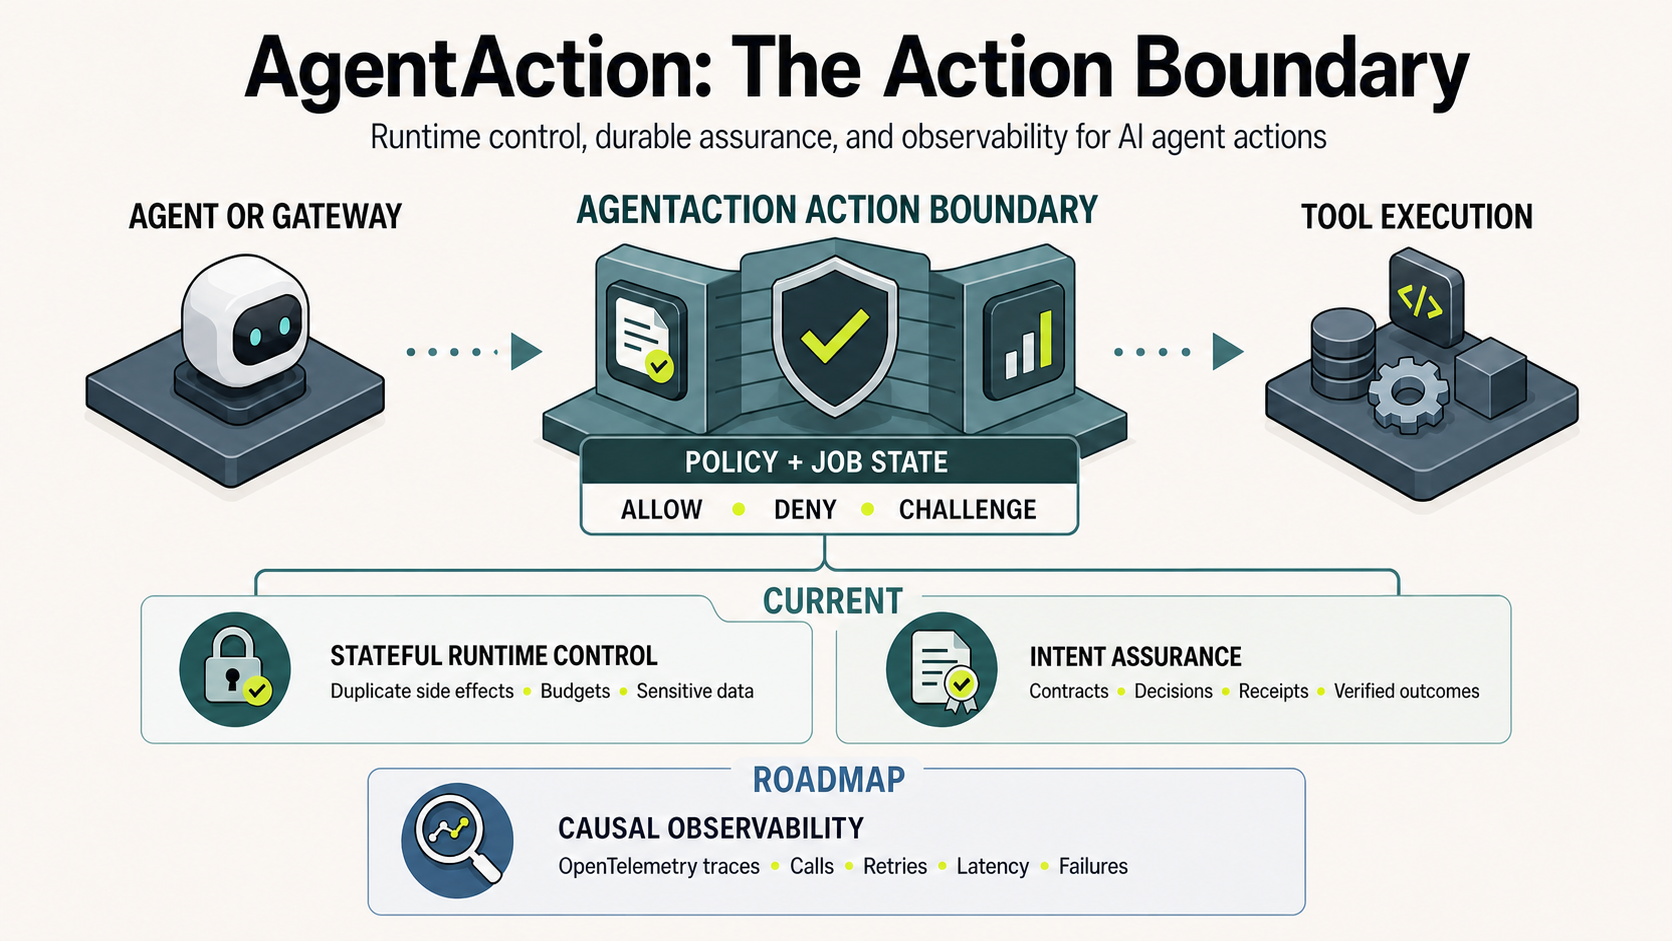
At enterprise scale, every consequential action crosses an enterprise-controlled gateway before reaching internal, SaaS, cloud, or provider-hosted tools. AgentAction acts as the decision service; the gateway remains the policy enforcement point, and providers can independently verify scoped authorization receipts.
AgentAction also fits into broader task-scoped security architectures such as Cloudflare's Agent Access Model (AAM). It implements the action-control and evidence layers while integrating with external identity brokers and network enforcement rather than replacing them.
Choose Your Path
| You are building | Start here |
|---|---|
| An existing MCP workflow or gateway | Start with the recommended passive observer quick start, then use the mcp-gateway-adapter/ integration guide |
| An agent or application | packages/guard/ and the local examples |
| An enterprise AI platform | Enterprise governance and authorization in practice |
| A SaaS, API, or MCP provider | Provider MCP authorization, Express middleware, or FastAPI helpers |
| An MCP server with unclear capabilities or limits | Capability inventory and workflow coverage: inspect the declared surface and find blockers in an explicitly mapped workflow |
| A security or risk program | Enterprise topology, receipt profiles, and standards alignment |
| An observability or assurance implementation | Intent assurance, the operator console, and community proposals |
For the enterprise CLI and manifest workflow:
git clone https://github.com/dinpd/AgentAction.git
cd AgentAction
python -m pip install -e ".[dev]"
agentaction validate examples/provider-mcp-support-agent.yaml
agentaction risk-score examples/provider-mcp-support-agent.yaml
agentaction generate-policy examples/provider-mcp-support-agent.yaml --target opa
The Python distribution is agentaction-dev. agentaction is the primary CLI.
agentpass and agentid remain compatibility aliases, and versioned schema,
environment-variable, and receipt identifiers retain their existing names.
Platform Control Surfaces
AgentAction exposes three connected control surfaces:
- Agent Evaluation: define versioned intent profiles, exercise synthetic scenarios, and compare profile-scoped assurance signals before wider deployment.
- Decision Assurance: assess the declared basis for a consequential choice, including policy factors, alternatives, assumptions, uncertainty, and supporting evidence—without inspecting hidden chain-of-thought.
- Action Authorization: gate the exact action against policy and prior state, then issue action-bound authority that providers can independently verify.
Provider verification, execution receipts, verified observations, immutable assessments, and outcome evaluation connect the three surfaces across the trust lifecycle. Framework wrappers, gateway adapters, and conformance suites are delivery and interoperability mechanisms, not separate product surfaces.
Current Capabilities
- Versioned intent profiles, synthetic scenarios, immutable assessments, and profile-scoped quality rollups provide the Agent Evaluation foundation.
- Normalized decision evidence captures policy factors, alternatives, assumptions, uncertainty, and supporting evidence without recording private chain-of-thought.
- Local TypeScript action authorization with circuit breakers, budgets, approvals, idempotency, PII/data-flow controls, and decision audit events.
- Passive observe and fail-closed enforce modes for MCP
tools/callthrough the reference MCP gateway adapter. - Cloudflare gateway runtime with tenant manifests, OIDC checks, approval queues, scoped JIT grants, audit timelines, and provider-result replay.
- Provider authorization receipts signed as JWS with a public JWKS endpoint.
- Express and FastAPI provider-side verification middleware.
- Versioned intent contracts, execution evidence, verified outcome observations, immutable snapshots, final evaluations, and quality rollups.
- Public synthetic-data observability demo plus an Access-protected operator console for fleet-level outcome, constraint, confidence, execution-discipline, and data-quality review.
- DevOps/SRE and OpenClaw solution packs for concrete integration paths.
See Current implementation status for planned and adopter-facing work.
Research
Jev vs LLMs for authorization decisions: synthetic approval workflows, live API measurements, raw evidence and reproducible evaluations. Experimental results; no production authorization changes.
Architecture And Documentation
- Enterprise deployment and governance
- Enterprise-managed MCP authorization sequence
- Action-gate roadmap
- Intent assurance
- Decision-basis evidence
- Provider contracts and authorization
- Agentic identity standards crosswalk
- Interoperability positioning
- Explainer video
Community Specifications And Roadmap
AgentAction publishes experimental, vendor-neutral drafts for Agent Action Boundary Evidence and Agent Outcome Observability and Assurance Metrics. They are discussion documents, not adopted standards; AgentAction is a non-normative reference implementation.
Implementation work and identified gaps are tracked in the public Intent Observability & Assurance project. The Action Gate Roadmap tracks product layers and adopter-facing demonstrations.
Open Source Governance
License
Apache-2.0
AgentAction MCP 질문
AgentAction이 자율형 agent에게 어떤 역할을 하나요?
AgentAction은 agent의 생애 주기 전반에 걸쳐 결정을 평가하고, 정책을 집행하며, 작업을 승인하고, 검증 가능한 증거를 보존하는 신뢰 계층 역할을 합니다.
AgentAction은 OAuth를 지원하나요?
OAuth discovery는 사용할 수 있지만, OAuth login은 아직 지원되지 않습니다.