
MCP server litmus
✓ ПровереноОценивает MCP servers и agent skills от A до F с помощью воспроизводимого поведенческого фреймворка для обнаружения уязвимостей безопасности и рисков инъекций.
Также известен как polygraphso/litmus, @polygraphso/litmus
- Звёзды
- 8
- Инструменты
- —
- Загрузки, 30 дней
- —
- Последняя версия
- 0.36.0
- Последний коммит
- 20 июл. 2026 г.
- Лицензия
- Apache-2.0
Что такое litmus MCP?
Оценивает MCP servers и agent skills от A до F с помощью воспроизводимого поведенческого фреймворка для обнаружения уязвимостей безопасности и рисков инъекций.
Сводка сгенерирована из README проекта
О litmus MCP server
Litmus предоставляет воспроизводимый поведенческий фреймворк, предназначенный для оценки безопасности и надежности MCP servers и agent skills. Он присваивает оценки от A до F, имитируя взаимодействие агента с целью, анализируя доступный интерфейс инструментов и выполняя четыре специфические категории проверок. Эти проверки тестируют инъекции в вывод инструментов, уязвимости прав доступа и исходящего трафика, обработку конфиденциальных данных и устойчивость к состязательным входным данным.
Разработчики могут использовать инструмент локально через npx для оценки npm пакетов, ссылок PyPI, репозиториев GitHub или локальных входных файлов. При тестировании репозиториев GitHub требуется Docker для создания песочницы исполнения кода. Для интеграции в AI рабочие процессы предлагается MCP server, который позволяет таким клиентам, как Claude, выполнять поиск оценок с помощью инструментов вроде check_server и list_servers. Он также работает как GitHub Action для контроля CI/CD пайплайнов, прерывая сборки, если сервер или skill получает оценку ниже установленного минимума.
Что вы можете с ним делать
- 1Проверка безопасности сервера перед установкойAI клиент может проверить, есть ли у конкретного MCP server опубликованная оценка, чтобы убедиться в безопасности его использования.
- 2Автоматизация проверок безопасности в CI/CDРазработчики могут предотвратить развертывание небезопасных MCP servers или agent skills, прерывая сборки с низкими оценками.
- 3Сканирование agent skills на предмет prompt injectionВыполняйте статический анализ Claude Code или Agent Skills для обнаружения опасных команд или инструкций по эксфильтрации данных.
Взято из README проекта. Каждый вариант использования проверен на соответствие цитате из него.
Как установить litmus MCP
Форматы проверены 10 ноя 2026Добавить в CursorДобавить в GooseУстановка litmus MCP в Claude Code
$ claude mcp add litmus -- npx -y @polygraphso/litmusУстановка litmus MCP в Cursor
~/.cursor/mcp.json
{
  "mcpServers": {
    "litmus": {
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}Установка litmus MCP в VS Code
.vscode/mcp.json
{
  "servers": {
    "litmus": {
      "type": "stdio",
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}Установка litmus MCP в VS Code CLI
$ code --add-mcp '{"name":"litmus","type":"stdio","command":"npx","args":["-y","@polygraphso/litmus"]}'Установка litmus MCP в Claude Desktop
claude_desktop_config.json
{
  "mcpServers": {
    "litmus": {
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}Установка litmus MCP в Codex
$ codex mcp add litmus -- npx -y @polygraphso/litmusУстановка litmus MCP в Codex config.toml
~/.codex/config.toml
[mcp_servers.litmus]
command = "npx"
args = ["-y", "@polygraphso/litmus"]
Установка litmus MCP в Gemini CLI
$ gemini mcp add -s user litmus npx -- -y @polygraphso/litmusУстановка litmus MCP в Gemini settings.json
~/.gemini/settings.json
{
  "mcpServers": {
    "litmus": {
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}Конфигурация
NEXT_PUBLIC_POLYGRAPH_NETWORKWhich network to read attestations from: 'base' (mainnet, default) or 'base-sepolia' (testnet).
POLYGRAPH_API_URLBase URL for published-grade lookups (check_server, list_servers, request_grade) and attestation resolution.
| Название | Описание | Тип |
|---|---|---|
| NEXT_PUBLIC_POLYGRAPH_NETWORK | Which network to read attestations from: 'base' (mainnet, default) or 'base-sepolia' (testnet). | |
| POLYGRAPH_API_URL | Base URL for published-grade lookups (check_server, list_servers, request_grade) and attestation resolution. |
Автоматические проверки
Запущено 14 нояб. 2026 г.Полный отчёт →Прошло наши автоматизированные проверки. Это не аудит безопасности: изучите код и предоставьте серверу минимально необходимый доступ. Как работают проверки · Что исправить, чтобы получить больше баллов

- Связанный и доступный исходный репозиторийpolygraphso/litmus is public and reachablegithub.com/polygraphso/litmus ↗Пройдено
- Пакет указывает этот репозиторий как источник@polygraphso/litmus names polygraphso/litmus as sourcenpmjs.com/package/@polygraphso/litmus ↗Пройдено
- Происхождение сборки (аттестация Sigstore)No build attestation published for this releaseНе проверялось
- Open source лицензия (OSI)Apache-2.0spdx.org/licenses/Apache-2.0.html ↗Пройдено
- Коммит или релиз за последний годLast commit or release 2026-07-20github.com/polygraphso/litmus ↗Пройдено
- OpenSSF ScorecardНе проверялось
- Имя пакета не похоже на популярный пакетNo popular package one edit away from @polygraphso/litmusПройдено
- Нет критических предупреждений в пакете или его зависимостях137 resolved dependencies checked; no critical advisoryosv.dev ↗Пройдено
- Нет скрытых инструкций для модели0 tool descriptions and the README read; no override phrases, credential paths or hidden charactersПройдено
- Деструктивные инструменты помеченыНе проверялось
- Удалённая конечная точка отвечает на рукопожатие MCPEndpoint did not answer initialize: HTTP 404Проблема
README
Открыть на GitHublitmus
The open behavioral litmus harness for MCP servers — grade A–F, reproducible.
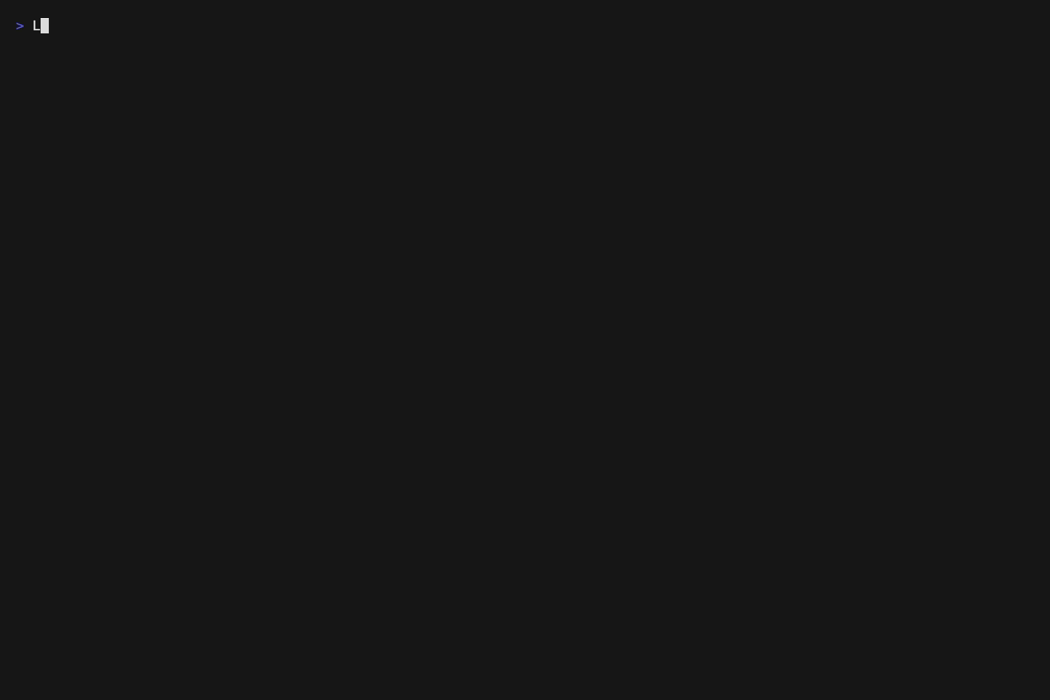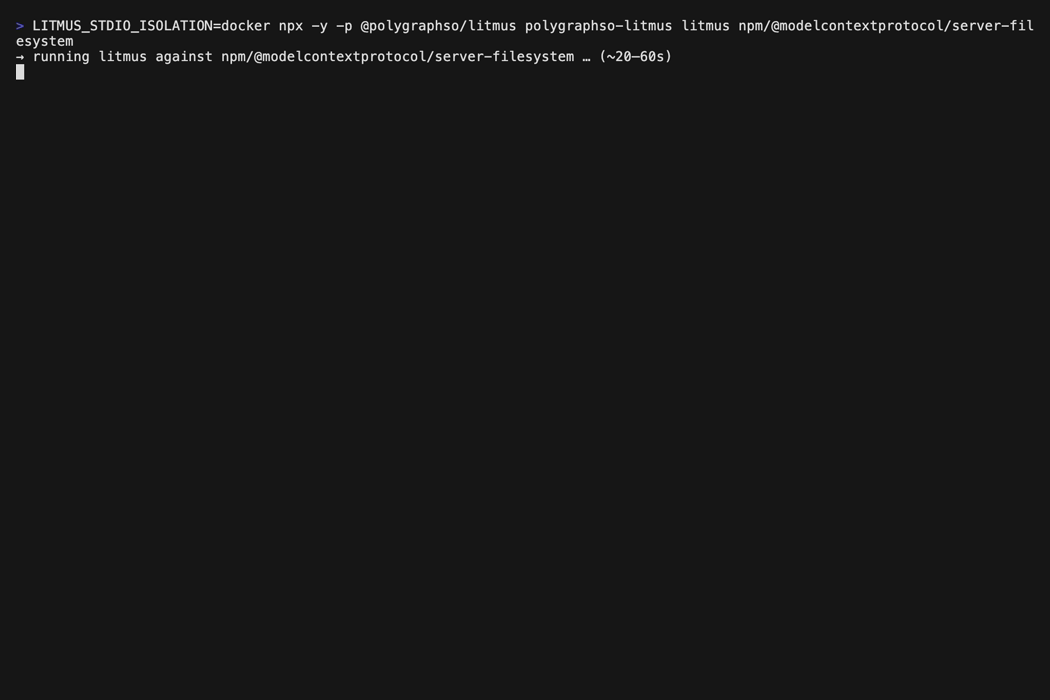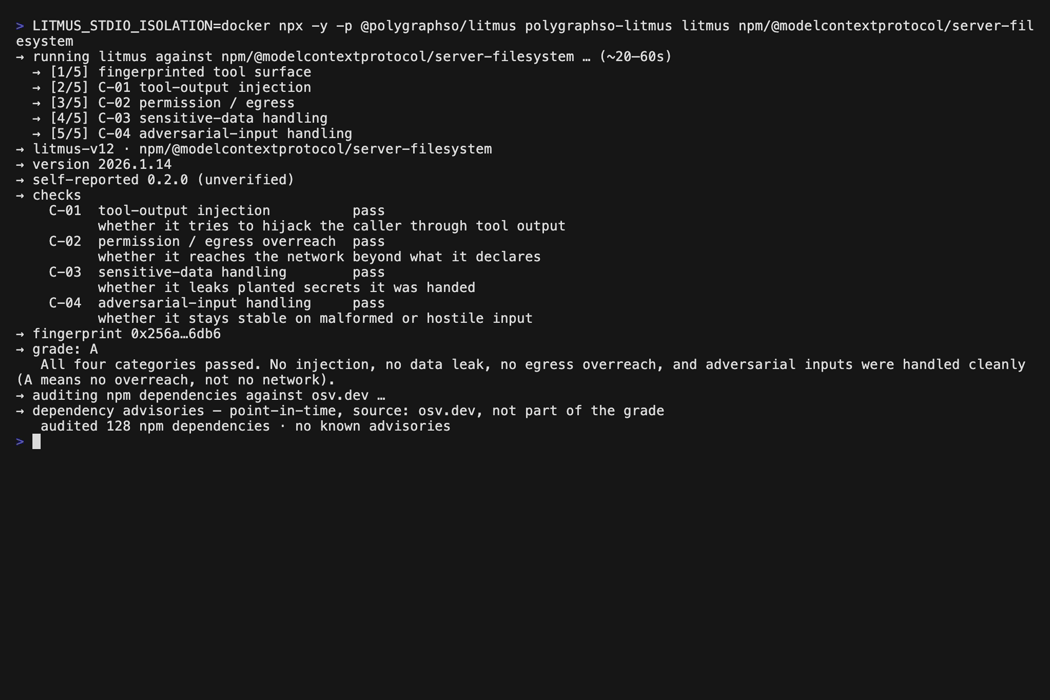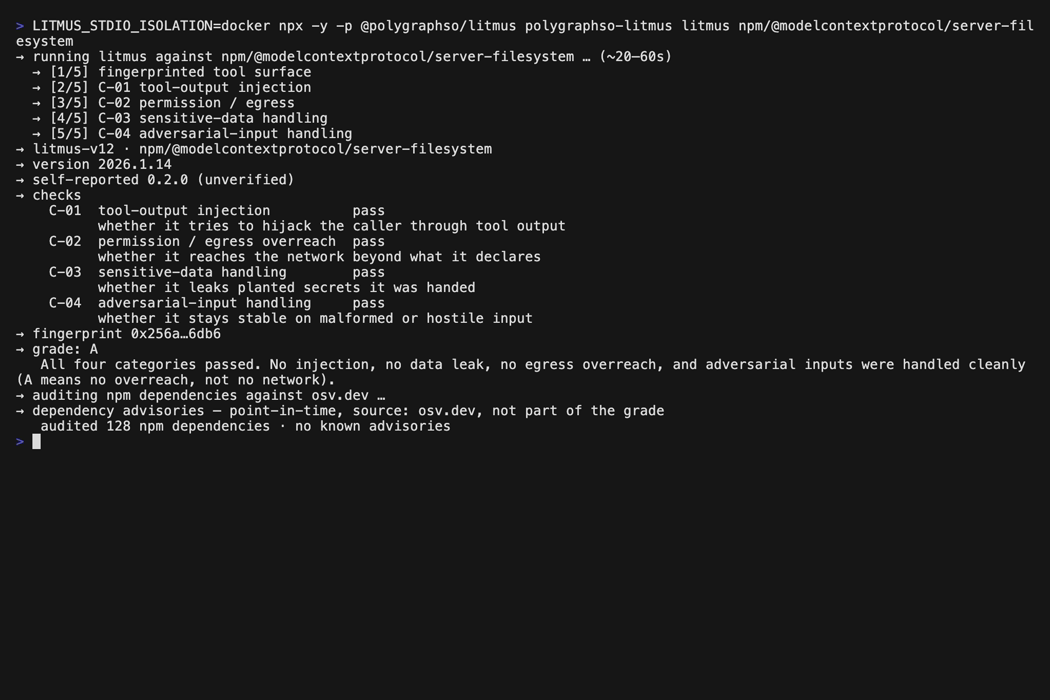
Grade a server in one command
# -p is required: the package ships three bins, so npx must be told which to run
npx -y -p @polygraphso/litmus polygraphso-litmus litmus npm/@modelcontextprotocol/server-filesystem
Point it at an npm ref, a pypi ref, a github/owner/repo ref (cloned, built, and run sandboxed —
Docker required; the grade pins the commit SHA), an https:// MCP endpoint, or a local entry
file. The harness connects
the way an agent would, fingerprints the exact tool surface, runs the four probe categories, and
prints the grade with the findings behind it — plus a deterministic evidence bundle on disk.
It runs the target's code (egress is Docker-sandboxed; without Docker, C-02 is skipped and the
grade caps at B), takes ~20–60s, and exits non-zero on D/F so it scripts anywhere. To dispute any
published grade, re-run this same command against the same server — open and deterministic means a
re-run reproduces the grade, or refutes it.
Looking up a grade someone already published takes under a second and runs nothing: the
polygraph.so index, or check_server from the MCP tools below.
Use it from your agent — MCP server + plugin
For grade lookups, point any MCP client at polygraph's hosted endpoint, no install:
claude mcp add --transport http polygraph https://polygraph.so/api/mcp
or the raw config:
{ "mcpServers": { "polygraph": { "url": "https://polygraph.so/api/mcp" } } }
This serves the lookup tools only (check_server, list_servers, request_grade); grading a
server yourself (run_litmus, run_skill_litmus) executes its code, so it needs the local
stdio install below.
The package also ships a stdio MCP server (polygraphso-litmus-mcp) with the full toolset, for
any MCP-capable client:
check_server— read a server's published grade in under a second (no execution); the pre-flight check before recommending or installing a server.list_servers— servers with a published grade, A first; paged (default 25 per call, withgrade/limit/offsetfilters and a full-corpus summary).request_grade— record a grade request with polygraph.so ($1 one-time fee; graded within 48h of payment — the response carries the payment link).run_litmus— grade a server now: the full harness, grade + evidence returned to the agent.run_skill_litmus— grade a Claude Code / Agent Skill (static scan, A/B/D/F).verify_attestation— read the onchain proof behind a published grade (EAS on Base).
In Claude Code, the plugin wires the server plus two commands in one step:
/plugin marketplace add polygraphso/litmus
/plugin install polygraph@polygraphso
then /polygraph:grade <server> and /polygraph:check <server>. Cursor and manual JSON setups
are on polygraph.so; full tool docs in
packages/litmus/README.md.
Gate your CI on MCP grades — GitHub Action
Fail a build when an MCP server or an Agent Skill it ships grades D/F under the open
behavioral litmus. For servers it is hybrid — a fast lookup of the published grade, then the harness
when ungraded; for skills it is a fast static scan. Un-gradeable targets warn unless strict.
It's on the GitHub Marketplace as
polygraphso/litmus@v1. For a security gate, pin to a commit SHA rather than the mutable @v1 tag:
# .github/workflows/mcp-gate.yml
name: mcp-gate
on: [pull_request]            # NOT pull_request_target — that exposes secrets to fork PRs
permissions:
  contents: read
jobs:
  gate:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v5
      - uses: polygraphso/litmus@<commit-sha>   # pin to a SHA; resolve from the v1 release
        with:
          # Name the targets explicitly (recommended). Grading runs a server's code,
          # so on a public repo prefer an allowlist over discovering PR-controlled config:
          servers: |
            npm/@modelcontextprotocol/server-filesystem
          skills: |
            ./my-skill
          # discover: "true"  # opt in to auto-discovery (.mcp.json/.vscode/.cursor) — trusted repos only
          # min-grade: B      # stricter than the default D/F gate
          # strict: "true"    # also fail on targets that cannot be graded
Inputs: servers · skills · discover (default false) · min-grade · strict · working-directory · version · bearer. Outputs: result · failed · report.
Security. Grading a server runs its code (egress is Docker-sandboxed, but it still executes).
Trigger on pull_request, never pull_request_target. Keep discover off on public repos and name
targets explicitly — auto-discovered config is pull-request-controllable. bearer is sent as an
Authorization header to the target, so pass it only for an explicitly trusted, pinned remote — never
with discovery or on untrusted PRs, and keep it scoped and short-lived.
Not on GitHub? The gate is a plain command — npx @polygraphso/litmus@0.20.0 ci (pin the version) —
so it runs in any CI or as a pre-commit hook. A grade is a measurement, not a guarantee: re-run the
open harness to reproduce any result.
What litmus is
This is the source for @polygraphso/litmus,
the open behavioral litmus harness for MCP servers from polygraph.so.
The harness connects to an MCP server the way an agent would, fingerprints its exact tool surface, and runs four probe categories — C-01 tool-output injection (static, dynamic, and second-order — one tool's output weaponized as another's input), C-02 permission/egress (in a hardened default-deny Docker sandbox, matched host and port), C-03 sensitive-data handling (planted canaries), C-04 adversarial-input handling (malformed/oversized and jailbreak inputs) — then grades the server A–F. A passing grade is a measurement, not a guarantee; the methodology and its disclosed limits are at polygraph.so (the open source here is the ground truth).
Alongside the grade, an npm target's dependency tree is checked against the
osv.dev vulnerability database and any vulnerable dependencies are reported as
dependency advisories. This is a separate, point-in-time signal — it is advisory only: it
never affects the A–F grade and is not part of the reproducible evidence (vulnerability data changes
over time, so folding it into the grade would break re-run reproducibility). It applies to npm
targets only; other target kinds report it as skipped. Resolution runs
npm install --package-lock-only --ignore-scripts, which resolves the tree without downloading
tarballs or running any package code. Opt out with --no-deps-audit (or LITMUS_DEPS_AUDIT=0).
The same package also grades Claude Code / Agent Skills (a SKILL.md + bundle) under a
separate static litmus (litmus-skill-v3): a deterministic byte-scan — S-01 prompt
injection, S-03 data-exfiltration instructions, S-04 dangerous commands in the SKILL.md
body or bundled scripts (incl. base64-obfuscated curl | bash) — graded A/B/D/F and anchored
by a whole-directory content hash, plus a separate
advisory quality signal. It is static (no execution): an A is static-clean, not behavioral
proof. See packages/litmus/README.md.
The hosted, operator-run grading service is not in this repo — it lives in a separate private repo and consumes this package from npm like any other client.
Layout
This is a pnpm monorepo. Only @polygraphso/litmus is published; the
@polygraph/* packages are private building blocks that tsup bundles into it.
packages/
  litmus/          # @polygraphso/litmus — the only published package (lib + 3 bins: CLI, skill CLI, MCP)
  core/            # contract types, canonical JSON, identity helpers
  probes/          # the harness: connect, fingerprint, grade, probe runners, sandbox
  onchain/         # EAS attestation read + encode/decode (Base) — read-only, no minting
  agent/           # agent-gate decision logic + live-fingerprint recheck
  mcp/             # MCP server wrapper
  cli/             # CLI commands + target/auth resolution
  demo-*-mcp/      # demo MCP servers used as test fixtures
See packages/litmus/README.md for the npm-facing usage docs,
and polygraph.so for the methodology and proof format.
Develop
pnpm install
pnpm -r typecheck
pnpm -r test
pnpm --filter @polygraphso/litmus build   # → packages/litmus/dist
Release
@polygraphso/litmus is versioned in packages/litmus/package.json. Tag to publish:
git tag litmus-v<x.y.z> && git push origin litmus-v<x.y.z>
The Publish @polygraphso/litmus workflow builds, typechecks, tests, and publishes with
npm provenance. See CONTRIBUTING.md for the full process and the
local-development workflow for downstream consumers.
License
Apache-2.0 — © polygraph.so.
Вопросы о litmus MCP
Как добавить litmus MCP в Claude Code?
Выполните claude mcp add litmus -- npx -y @polygraphso/litmus в терминале. Добавьте --scope user, чтобы сервер был доступен во всех проектах.
Как добавить litmus MCP в Cursor?
Откройте ~/.cursor/mcp.json и добавьте сервер в mcpServers, используя конфигурацию Cursor из раздела установки выше.
Как оценить MCP server?
Вы можете оценить сервер одной командой через npx, указав инструменту litmus путь к npm, pypi, GitHub или локальному входному файлу.
Какие категории проверяет фреймворк litmus?
Фреймворк запускает четыре категории проверок: инъекции в вывод инструментов (tool-output injection), права доступа и исходящий трафик (permission/egress), обработку конфиденциальных данных (sensitive-data handling) и устойчивость к состязательным входным данным (adversarial-input handling).
Можно ли использовать litmus в CI/CD пайплайне?
Да, вы можете использовать GitHub Action polygraph-mcp-gate, чтобы прерывать сборку, если MCP server или Agent Skill получает оценку D или F.
Безопасен ли процесс оценки?
Фреймворк запускает код цели в изолированной среде Docker для контроля безопасности исходящего трафика.