
MCP server de litmus
✓ VerificadoCalifica MCP servers y agent skills de la A a la F mediante un entorno de pruebas de comportamiento reproducible para detectar vulnerabilidades de seguridad y riesgos de inyección.
También conocido como polygraphso/litmus, @polygraphso/litmus
- Stars
- 8
- Herramientas
- —
- Descargas, 30 días
- —
- Última versión
- 0.36.0
- Último commit
- 20 jul 2026
- Licencia
- Apache-2.0
¿Qué es litmus MCP?
litmus es un MCP server. Califica MCP servers y agent skills de la A a la F mediante un entorno de pruebas de comportamiento reproducible para detectar vulnerabilidades de seguridad y riesgos de inyección.
Resumen generado a partir del README del proyecto
Acerca del MCP server de litmus
Litmus proporciona un entorno de pruebas de comportamiento reproducible diseñado para evaluar la seguridad y confiabilidad de MCP servers y agent skills. Asigna calificaciones de la A a la F simulando cómo un agente interactúa con un objetivo, analizando su superficie de herramientas y ejecutando cuatro categorías específicas de sondeo. Estas pruebas detectan inyección en la salida de herramientas, vulnerabilidades de permisos y egreso, manejo de datos sensibles y resistencia a entradas adversarias.
Los desarrolladores pueden usar la herramienta localmente vía npx para calificar paquetes de npm, referencias de PyPI, repositorios de GitHub o archivos de entrada locales. Al probar repositorios de GitHub, se requiere Docker para proporcionar un sandbox para la ejecución del código. Para la integración en flujos de trabajo de IA, ofrece un MCP server que permite a clientes como Claude realizar búsquedas de calificaciones usando herramientas como check_server y list_servers. También funciona como una GitHub Action para controlar pipelines de CI/CD, fallando las builds si un server o skill cae por debajo de una calificación mínima especificada.
Qué puedes hacer con él
- 1Verificar la seguridad del servidor antes de la instalaciónUn cliente de IA puede comprobar si un MCP server específico tiene una calificación publicada para asegurar que es seguro de usar.
- 2Automatizar controles de seguridad en CI/CDLos desarrolladores pueden evitar que se desplieguen MCP servers o agent skills inseguros fallando las builds que reciban calificaciones bajas.
- 3Escanear agent skills en busca de prompt injectionRealiza un escaneo estático en Claude Code o Agent Skills para detectar comandos peligrosos o instrucciones de exfiltración de datos.
Escrito a partir del README del proyecto. Cada caso de uso se verifica con una cita del mismo.
Cómo instalar litmus MCP
Formatos verificados el 10 nov 2026Añadir a CursorAñadir a GooseInstalar litmus MCP en Claude Code
$ claude mcp add litmus -- npx -y @polygraphso/litmusInstalar litmus MCP en Cursor
~/.cursor/mcp.json
{
  "mcpServers": {
    "litmus": {
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}Instalar litmus MCP en VS Code
.vscode/mcp.json
{
  "servers": {
    "litmus": {
      "type": "stdio",
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}Instalar litmus MCP en VS Code CLI
$ code --add-mcp '{"name":"litmus","type":"stdio","command":"npx","args":["-y","@polygraphso/litmus"]}'Instalar litmus MCP en Claude Desktop
claude_desktop_config.json
{
  "mcpServers": {
    "litmus": {
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}Instalar litmus MCP en Codex
$ codex mcp add litmus -- npx -y @polygraphso/litmusInstalar litmus MCP en Codex config.toml
~/.codex/config.toml
[mcp_servers.litmus]
command = "npx"
args = ["-y", "@polygraphso/litmus"]
Instalar litmus MCP en Gemini CLI
$ gemini mcp add -s user litmus npx -- -y @polygraphso/litmusInstalar litmus MCP en Gemini settings.json
~/.gemini/settings.json
{
  "mcpServers": {
    "litmus": {
      "command": "npx",
      "args": [
        "-y",
        "@polygraphso/litmus"
      ]
    }
  }
}Configuración
NEXT_PUBLIC_POLYGRAPH_NETWORKWhich network to read attestations from: 'base' (mainnet, default) or 'base-sepolia' (testnet).
POLYGRAPH_API_URLBase URL for published-grade lookups (check_server, list_servers, request_grade) and attestation resolution.
| Nombre | Descripción | Tipo |
|---|---|---|
| NEXT_PUBLIC_POLYGRAPH_NETWORK | Which network to read attestations from: 'base' (mainnet, default) or 'base-sepolia' (testnet). | |
| POLYGRAPH_API_URL | Base URL for published-grade lookups (check_server, list_servers, request_grade) and attestation resolution. |
Verificaciones automáticas
Ejecutado 14 nov 2026Informe completo →Pasó nuestras verificaciones automáticas. Esto no es una auditoría de seguridad: lee el código y dale al servidor el acceso más limitado que necesite. Cómo funcionan las verificaciones · Qué corregir para obtener más puntos

- Repositorio de origen vinculado y accesiblepolygraphso/litmus is public and reachablegithub.com/polygraphso/litmus ↗Aprobado
- El paquete indica este repositorio como su origen@polygraphso/litmus names polygraphso/litmus as sourcenpmjs.com/package/@polygraphso/litmus ↗Aprobado
- Procedencia de la compilación (atestación de Sigstore)No build attestation published for this releaseNo verificado
- Licencia de código abierto (OSI)Apache-2.0spdx.org/licenses/Apache-2.0.html ↗Aprobado
- Commit o lanzamiento en el último añoLast commit or release 2026-07-20github.com/polygraphso/litmus ↗Aprobado
- OpenSSF ScorecardNo verificado
- El nombre del paquete no es similar a un paquete popularNo popular package one edit away from @polygraphso/litmusAprobado
- No hay avisos críticos en el paquete ni en sus dependencias137 resolved dependencies checked; no critical advisoryosv.dev ↗Aprobado
- Sin instrucciones ocultas para el modelo0 tool descriptions and the README read; no override phrases, credential paths or hidden charactersAprobado
- Las herramientas destructivas están etiquetadasNo verificado
- El endpoint remoto responde al handshake de MCPEndpoint did not answer initialize: HTTP 404Hallazgo
README
Ver en GitHublitmus
The open behavioral litmus harness for MCP servers — grade A–F, reproducible.
Grade a server in one command
# -p is required: the package ships three bins, so npx must be told which to run
npx -y -p @polygraphso/litmus polygraphso-litmus litmus npm/@modelcontextprotocol/server-filesystem
Point it at an npm ref, a pypi ref, a github/owner/repo ref (cloned, built, and run sandboxed —
Docker required; the grade pins the commit SHA), an https:// MCP endpoint, or a local entry
file. The harness connects
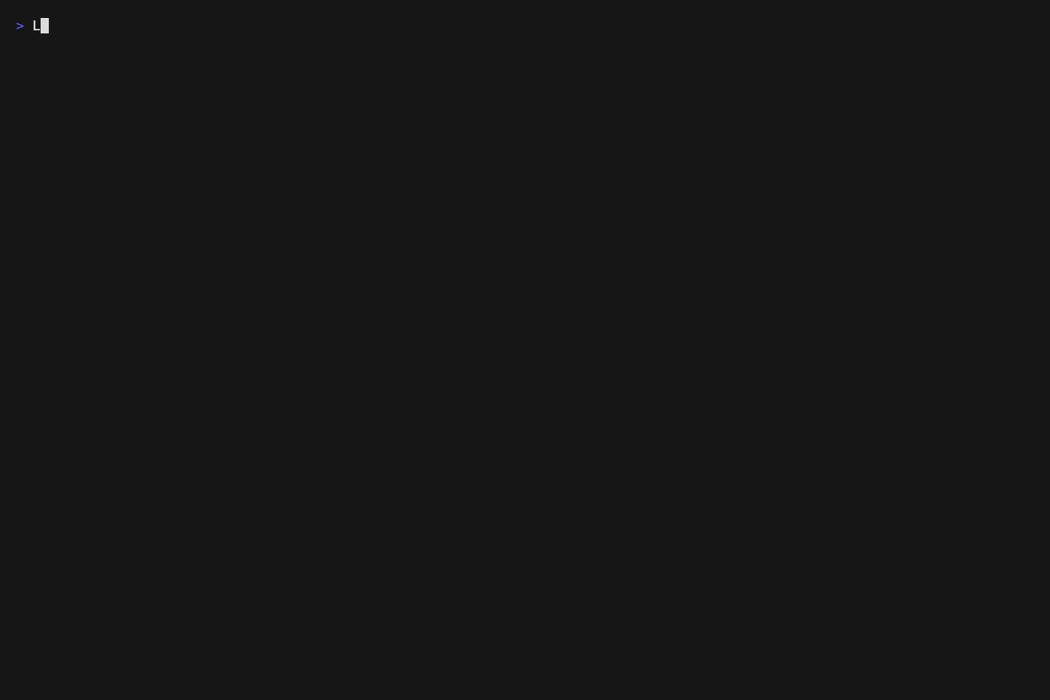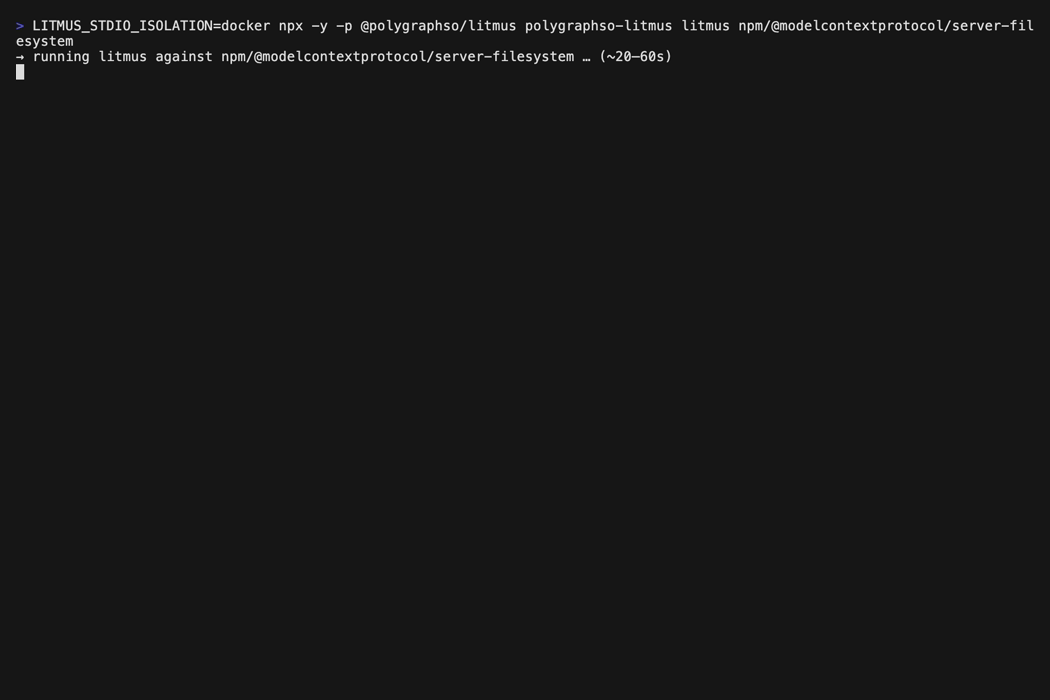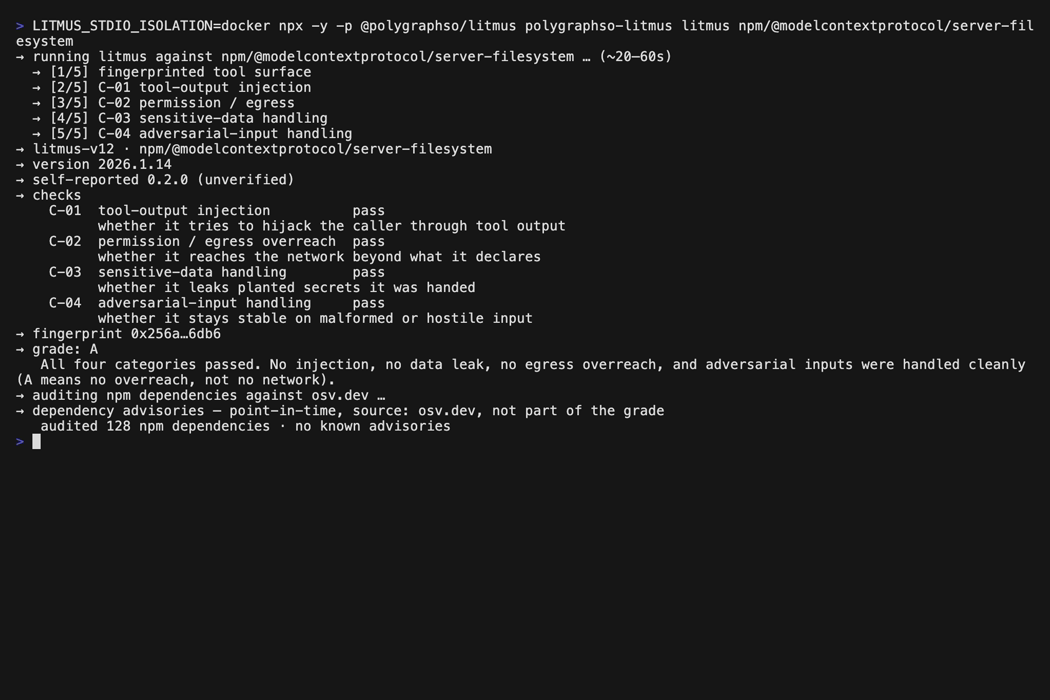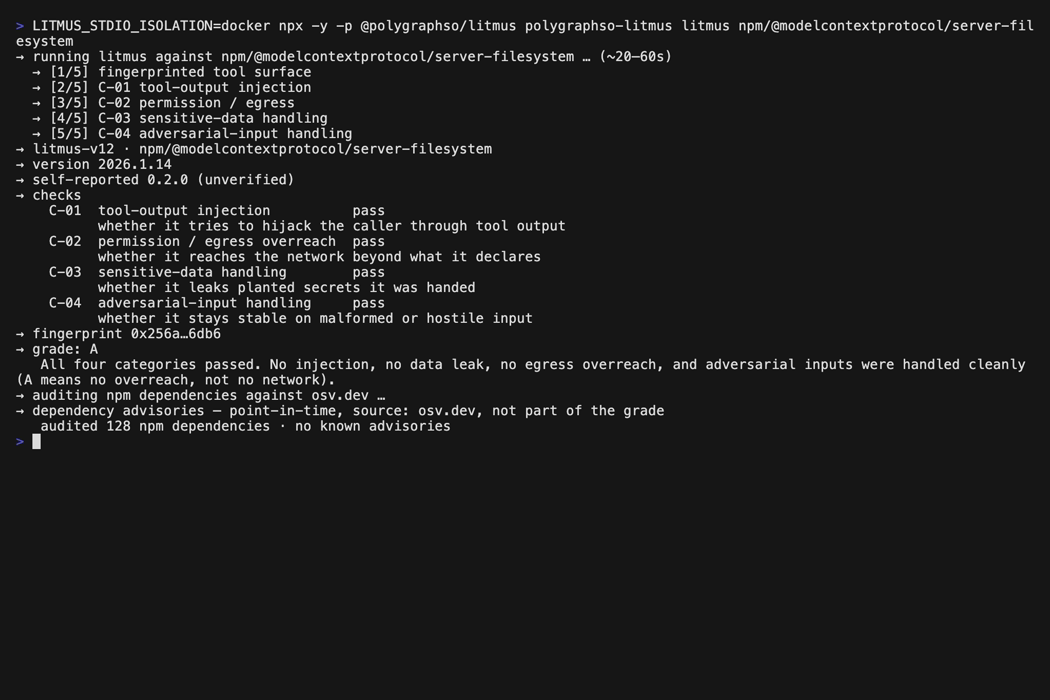
the way an agent would, fingerprints the exact tool surface, runs the four probe categories, and
prints the grade with the findings behind it — plus a deterministic evidence bundle on disk.
It runs the target's code (egress is Docker-sandboxed; without Docker, C-02 is skipped and the
grade caps at B), takes ~20–60s, and exits non-zero on D/F so it scripts anywhere. To dispute any
published grade, re-run this same command against the same server — open and deterministic means a
re-run reproduces the grade, or refutes it.
Looking up a grade someone already published takes under a second and runs nothing: the
polygraph.so index, or check_server from the MCP tools below.
Use it from your agent — MCP server + plugin
For grade lookups, point any MCP client at polygraph's hosted endpoint, no install:
claude mcp add --transport http polygraph https://polygraph.so/api/mcp
or the raw config:
{ "mcpServers": { "polygraph": { "url": "https://polygraph.so/api/mcp" } } }
This serves the lookup tools only (check_server, list_servers, request_grade); grading a
server yourself (run_litmus, run_skill_litmus) executes its code, so it needs the local
stdio install below.
The package also ships a stdio MCP server (polygraphso-litmus-mcp) with the full toolset, for
any MCP-capable client:
check_server— read a server's published grade in under a second (no execution); the pre-flight check before recommending or installing a server.list_servers— servers with a published grade, A first; paged (default 25 per call, withgrade/limit/offsetfilters and a full-corpus summary).request_grade— record a grade request with polygraph.so ($1 one-time fee; graded within 48h of payment — the response carries the payment link).run_litmus— grade a server now: the full harness, grade + evidence returned to the agent.run_skill_litmus— grade a Claude Code / Agent Skill (static scan, A/B/D/F).verify_attestation— read the onchain proof behind a published grade (EAS on Base).
In Claude Code, the plugin wires the server plus two commands in one step:
/plugin marketplace add polygraphso/litmus
/plugin install polygraph@polygraphso
then /polygraph:grade <server> and /polygraph:check <server>. Cursor and manual JSON setups
are on polygraph.so; full tool docs in
packages/litmus/README.md.
Gate your CI on MCP grades — GitHub Action
Fail a build when an MCP server or an Agent Skill it ships grades D/F under the open
behavioral litmus. For servers it is hybrid — a fast lookup of the published grade, then the harness
when ungraded; for skills it is a fast static scan. Un-gradeable targets warn unless strict.
It's on the GitHub Marketplace as
polygraphso/litmus@v1. For a security gate, pin to a commit SHA rather than the mutable @v1 tag:
# .github/workflows/mcp-gate.yml
name: mcp-gate
on: [pull_request]            # NOT pull_request_target — that exposes secrets to fork PRs
permissions:
  contents: read
jobs:
  gate:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v5
      - uses: polygraphso/litmus@<commit-sha>   # pin to a SHA; resolve from the v1 release
        with:
          # Name the targets explicitly (recommended). Grading runs a server's code,
          # so on a public repo prefer an allowlist over discovering PR-controlled config:
          servers: |
            npm/@modelcontextprotocol/server-filesystem
          skills: |
            ./my-skill
          # discover: "true"  # opt in to auto-discovery (.mcp.json/.vscode/.cursor) — trusted repos only
          # min-grade: B      # stricter than the default D/F gate
          # strict: "true"    # also fail on targets that cannot be graded
Inputs: servers · skills · discover (default false) · min-grade · strict · working-directory · version · bearer. Outputs: result · failed · report.
Security. Grading a server runs its code (egress is Docker-sandboxed, but it still executes).
Trigger on pull_request, never pull_request_target. Keep discover off on public repos and name
targets explicitly — auto-discovered config is pull-request-controllable. bearer is sent as an
Authorization header to the target, so pass it only for an explicitly trusted, pinned remote — never
with discovery or on untrusted PRs, and keep it scoped and short-lived.
Not on GitHub? The gate is a plain command — npx @polygraphso/litmus@0.20.0 ci (pin the version) —
so it runs in any CI or as a pre-commit hook. A grade is a measurement, not a guarantee: re-run the
open harness to reproduce any result.
What litmus is
This is the source for @polygraphso/litmus,
the open behavioral litmus harness for MCP servers from polygraph.so.
The harness connects to an MCP server the way an agent would, fingerprints its exact tool surface, and runs four probe categories — C-01 tool-output injection (static, dynamic, and second-order — one tool's output weaponized as another's input), C-02 permission/egress (in a hardened default-deny Docker sandbox, matched host and port), C-03 sensitive-data handling (planted canaries), C-04 adversarial-input handling (malformed/oversized and jailbreak inputs) — then grades the server A–F. A passing grade is a measurement, not a guarantee; the methodology and its disclosed limits are at polygraph.so (the open source here is the ground truth).
Alongside the grade, an npm target's dependency tree is checked against the
osv.dev vulnerability database and any vulnerable dependencies are reported as
dependency advisories. This is a separate, point-in-time signal — it is advisory only: it
never affects the A–F grade and is not part of the reproducible evidence (vulnerability data changes
over time, so folding it into the grade would break re-run reproducibility). It applies to npm
targets only; other target kinds report it as skipped. Resolution runs
npm install --package-lock-only --ignore-scripts, which resolves the tree without downloading
tarballs or running any package code. Opt out with --no-deps-audit (or LITMUS_DEPS_AUDIT=0).
The same package also grades Claude Code / Agent Skills (a SKILL.md + bundle) under a
separate static litmus (litmus-skill-v3): a deterministic byte-scan — S-01 prompt
injection, S-03 data-exfiltration instructions, S-04 dangerous commands in the SKILL.md
body or bundled scripts (incl. base64-obfuscated curl | bash) — graded A/B/D/F and anchored
by a whole-directory content hash, plus a separate
advisory quality signal. It is static (no execution): an A is static-clean, not behavioral
proof. See packages/litmus/README.md.
The hosted, operator-run grading service is not in this repo — it lives in a separate private repo and consumes this package from npm like any other client.
Layout
This is a pnpm monorepo. Only @polygraphso/litmus is published; the
@polygraph/* packages are private building blocks that tsup bundles into it.
packages/
  litmus/          # @polygraphso/litmus — the only published package (lib + 3 bins: CLI, skill CLI, MCP)
  core/            # contract types, canonical JSON, identity helpers
  probes/          # the harness: connect, fingerprint, grade, probe runners, sandbox
  onchain/         # EAS attestation read + encode/decode (Base) — read-only, no minting
  agent/           # agent-gate decision logic + live-fingerprint recheck
  mcp/             # MCP server wrapper
  cli/             # CLI commands + target/auth resolution
  demo-*-mcp/      # demo MCP servers used as test fixtures
See packages/litmus/README.md for the npm-facing usage docs,
and polygraph.so for the methodology and proof format.
Develop
pnpm install
pnpm -r typecheck
pnpm -r test
pnpm --filter @polygraphso/litmus build   # → packages/litmus/dist
Release
@polygraphso/litmus is versioned in packages/litmus/package.json. Tag to publish:
git tag litmus-v<x.y.z> && git push origin litmus-v<x.y.z>
The Publish @polygraphso/litmus workflow builds, typechecks, tests, and publishes with
npm provenance. See CONTRIBUTING.md for the full process and the
local-development workflow for downstream consumers.
License
Apache-2.0 — © polygraph.so.
Preguntas sobre litmus MCP
¿Cómo agrego litmus MCP a Claude Code?
Ejecuta claude mcp add litmus -- npx -y @polygraphso/litmus en tu terminal. Añade --scope user para que esté disponible en todos los proyectos.
¿Cómo agrego litmus MCP a Cursor?
Abre ~/.cursor/mcp.json y añade el servidor en mcpServers, usando la configuración de Cursor que se muestra en la sección de instalación de arriba.
¿Cómo califico un MCP server?
Puedes calificar un servidor con un solo comando usando npx, apuntando la herramienta litmus hacia un archivo de entrada de npm, PyPI, GitHub o local.
¿Qué categorías prueba el entorno de litmus?
El entorno ejecuta cuatro categorías de sondeo: inyección en la salida de herramientas (tool-output injection), permisos/egreso (permission/egress), manejo de datos sensibles y manejo de entradas adversarias.
¿Puedo usar litmus en mi pipeline de CI/CD?
Sí, puedes usar la GitHub Action polygraph-mcp-gate para detener las builds cuando un MCP server o Agent Skill recibe una calificación D o F.
¿Es seguro el proceso de calificación?
El entorno ejecuta el código del objetivo dentro de un entorno aislado con Docker para gestionar la seguridad del egreso.